
Managed Services
MSP Cuts Vendor Access Risk with Brokered JIT Sessions
How a managed service provider replaced shared credentials and standing VPN access with time-boxed, fully recorded vendor sessions.
Zenxsys · September 5, 2026 · 4 min read
- Standing vendor VPN access eliminated
- 100% of privileged vendor sessions recorded
- Access-request-to-grant time reduced to minutes
This is a sample case study. Replace with a real customer story from the CMS.
Challenge
The provider managed infrastructure for dozens of clients and relied on shared credentials and always-on VPN access for third-party engineers - with little visibility into who did what.
Solution
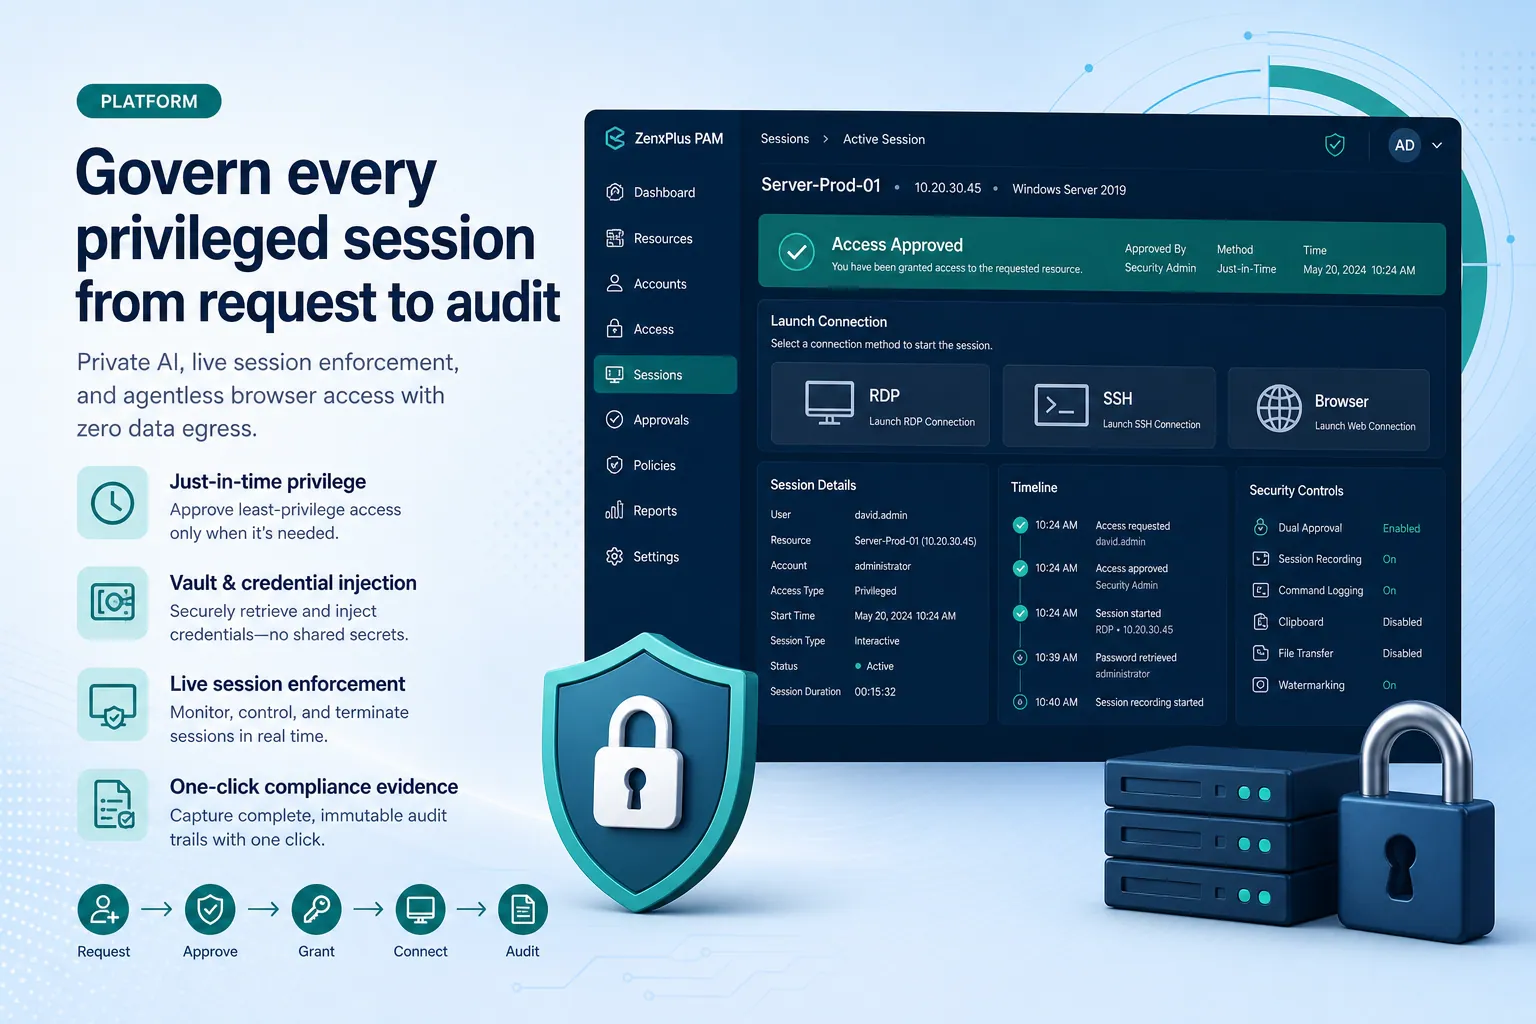
Using ZenXPAM, the team moved to brokered, just-in-time sessions: vendors request access to a specific target for a specific window, credentials stay vaulted, and every session is recorded.
Results
Standing access was eliminated, every privileged session became auditable, and access provisioning dropped from days to minutes.