Threat Detection & Investigation
Detect anomalous behavior. Reconstruct what happened. Export the report.
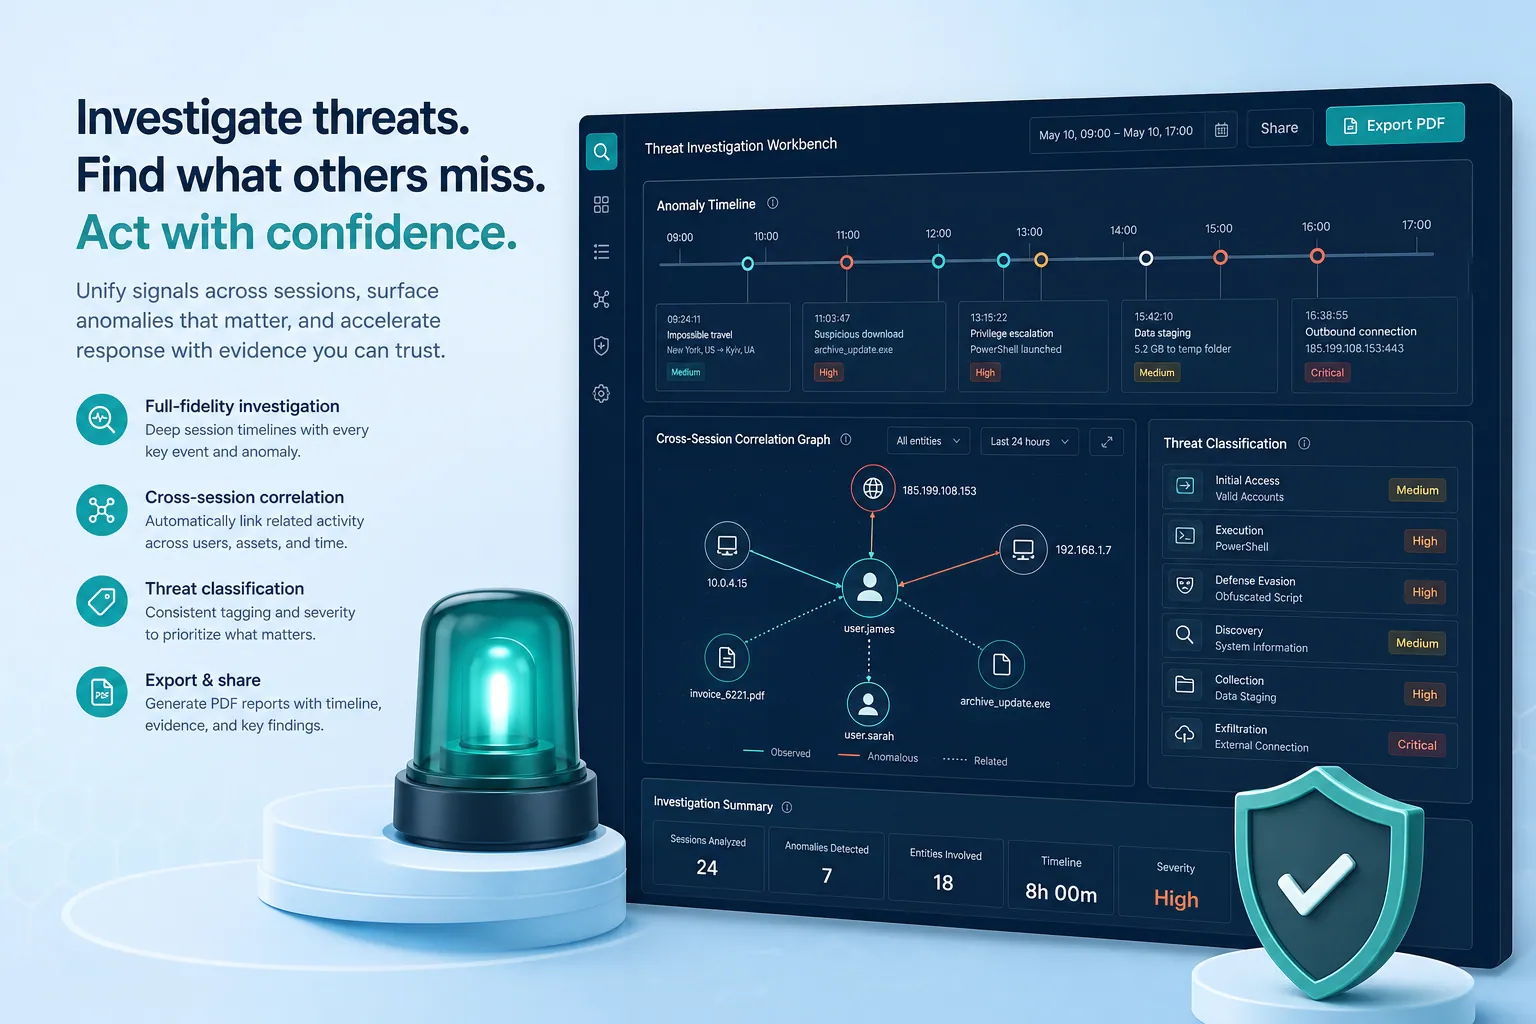
Distinct from session recording. Behavior analysis, anomaly detection, threat classification, and cross-session event correlation feed a full investigation workbench - timeline reconstruction, pattern detection, and PDF report export. Recording watches. This detects and investigates.
Detect
Behavior & anomalies
Correlate
Cross-session events
Timeline
Investigation UI
Forensic reports
How it works
Behavior analysis & anomaly detection
Classify threats from real privileged-session behavior - not just store recordings for someone to review later.
Cross-session correlation
Connect events across sessions so investigations see the pattern, not a pile of isolated clips.
Investigation workbench
Timeline reconstruction and pattern detection in a dedicated forensic UI built for security responders.
PDF report export
Hand leadership and auditors a structured investigation report - not a zip of raw logs.
Why it's different
Session recording only implies watching. This is UEBA-adjacent detection and investigation - the story security teams actually need after the first alert.
Built for
SOC and identity security teams who need to move from “we recorded it” to “we detected it and can prove what happened.”
- Behavior analysis & anomaly detection
- Cross-session correlation
- Investigation workbench
- PDF report export