
Zenxsys Products
Real platforms and capabilities for privileged access & knowledge
ZenXPAM, ZenXEKA, and ZenXPages - plus focused ZenxPlus capabilities built into how we secure sessions, secrets, vendors, and compliance evidence.
Local
AI runs inside your own deployment
JIT
Time-boxed privilege, not standing admin
Live
In-session enforcement, not post-hoc review
Agentless
Browser RDP, SSH & RemoteApp access
Flagship platform
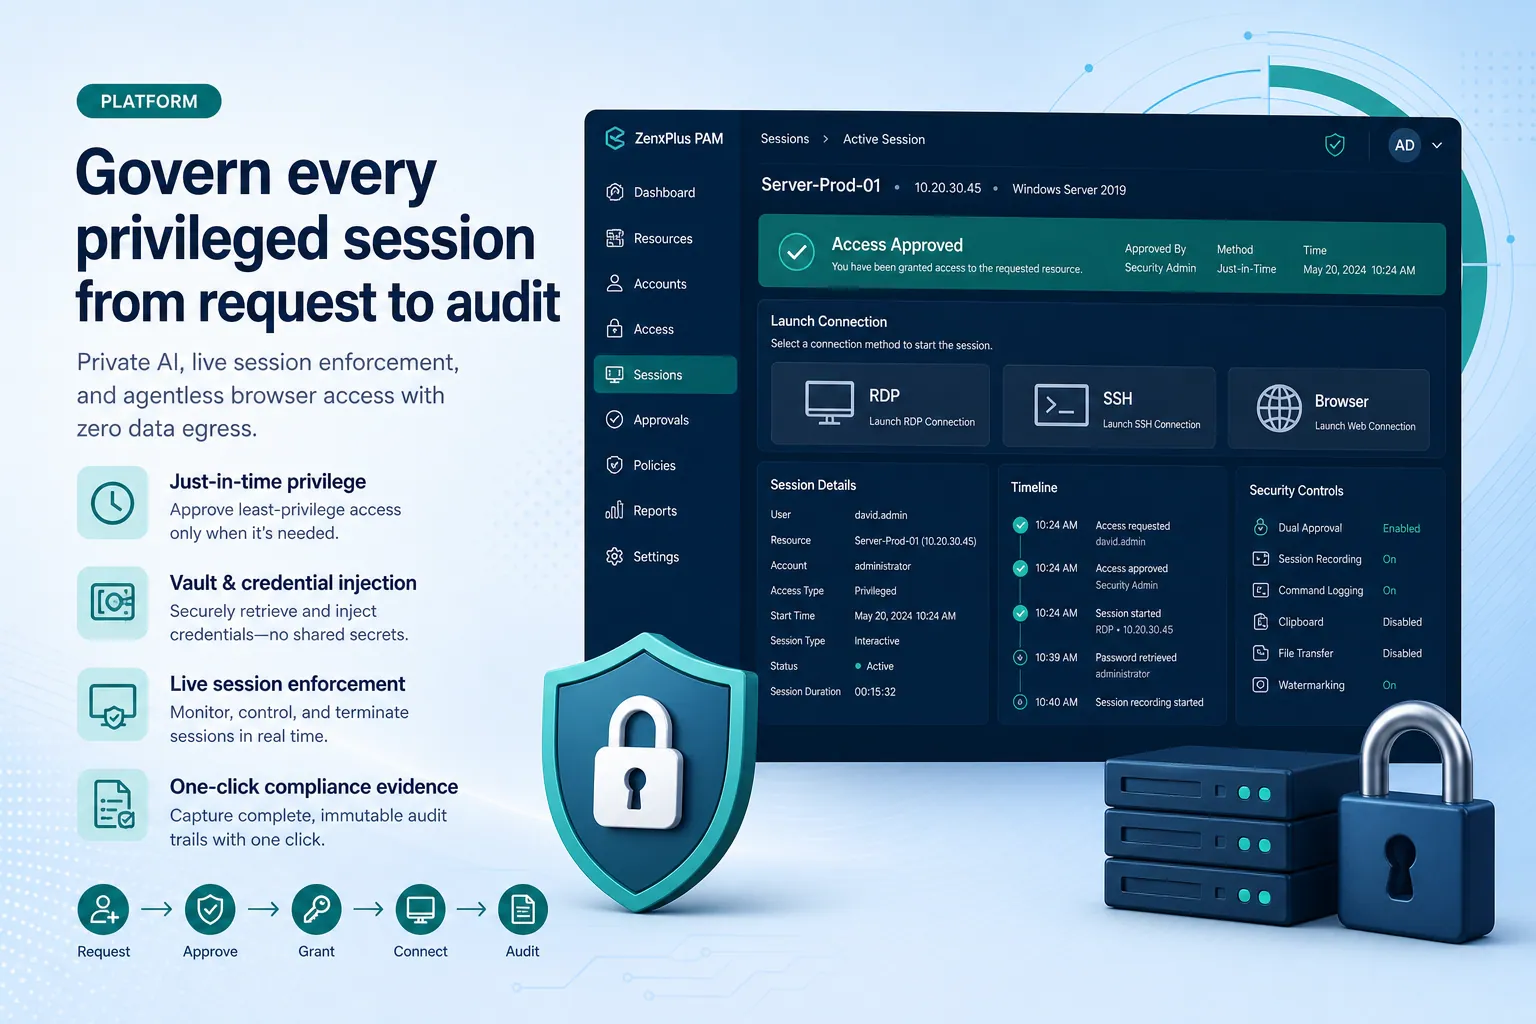
ZenXPAM (PAM)
Govern every privileged session - from request to audit
Enterprise-grade privileged access for cloud-native, hybrid, and on-premises environments. Local-first AI, live session enforcement, and agentless browser access - with signed, audit-ready evidence built in.
- Just-in-Time privilege management
- Privileged access brokering
- Vault, rotation & credentials
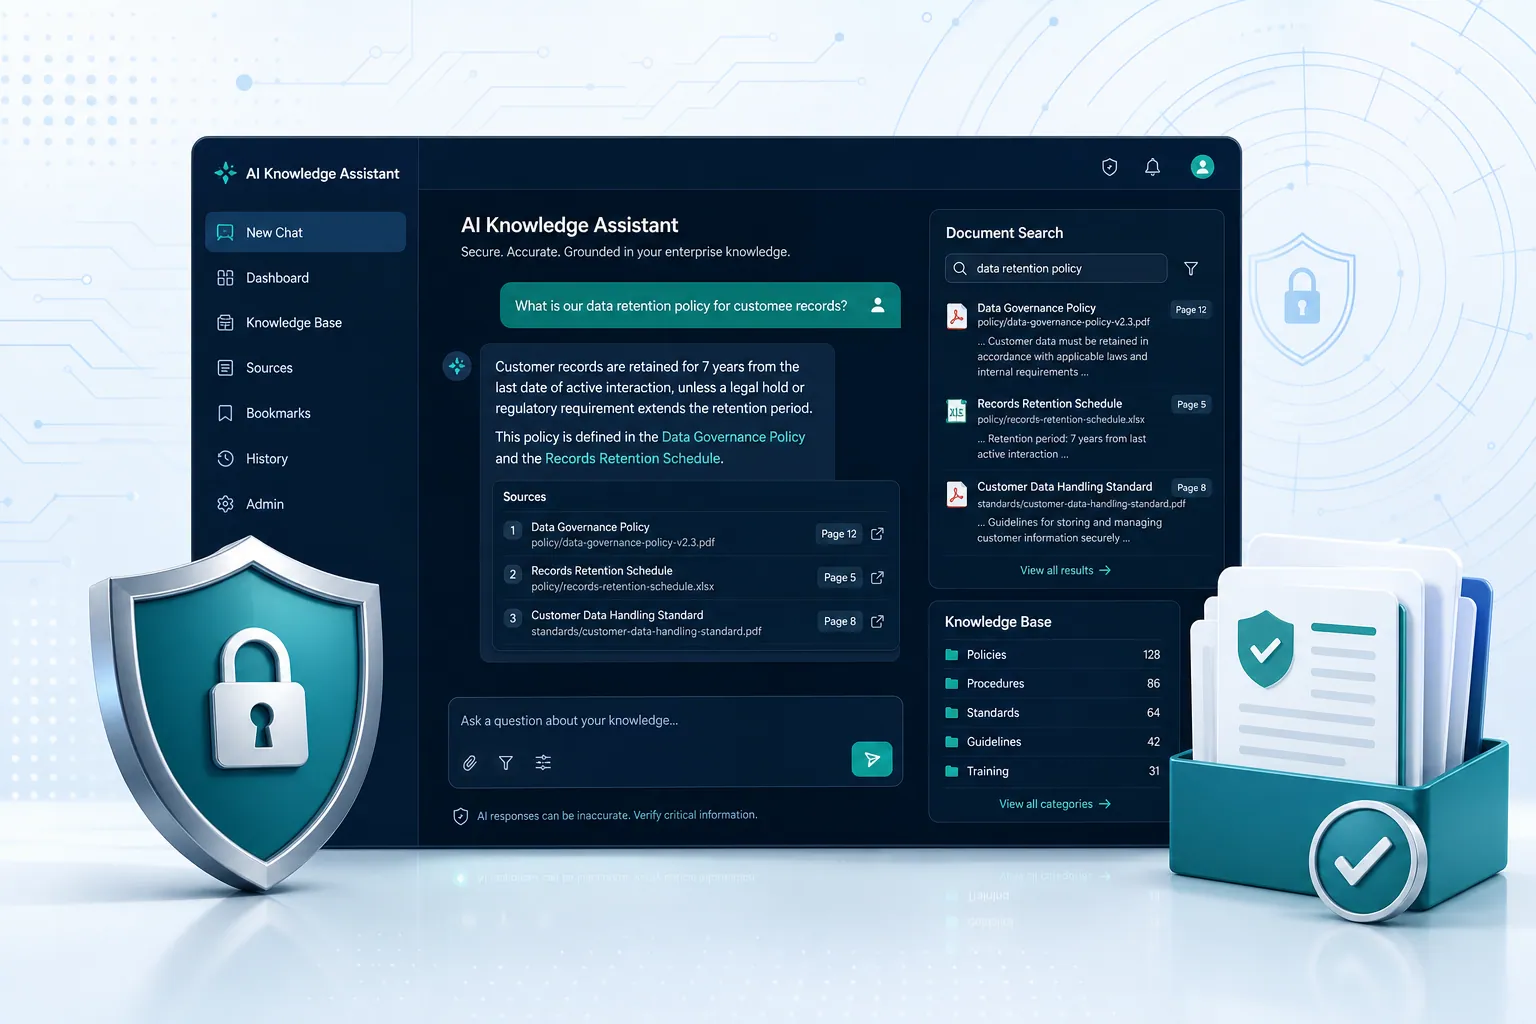
Enterprise Knowledge Assistant (ZenXEKA)
Answers from your knowledge - with enterprise security controls
ZenXEKA is Zenxsys’ flagship knowledge product: AI-powered search and assistance over your enterprise content, designed for secure, governed deployment.
- Enterprise knowledge retrieval
- Security-aware deployment
- Fast, practical responses
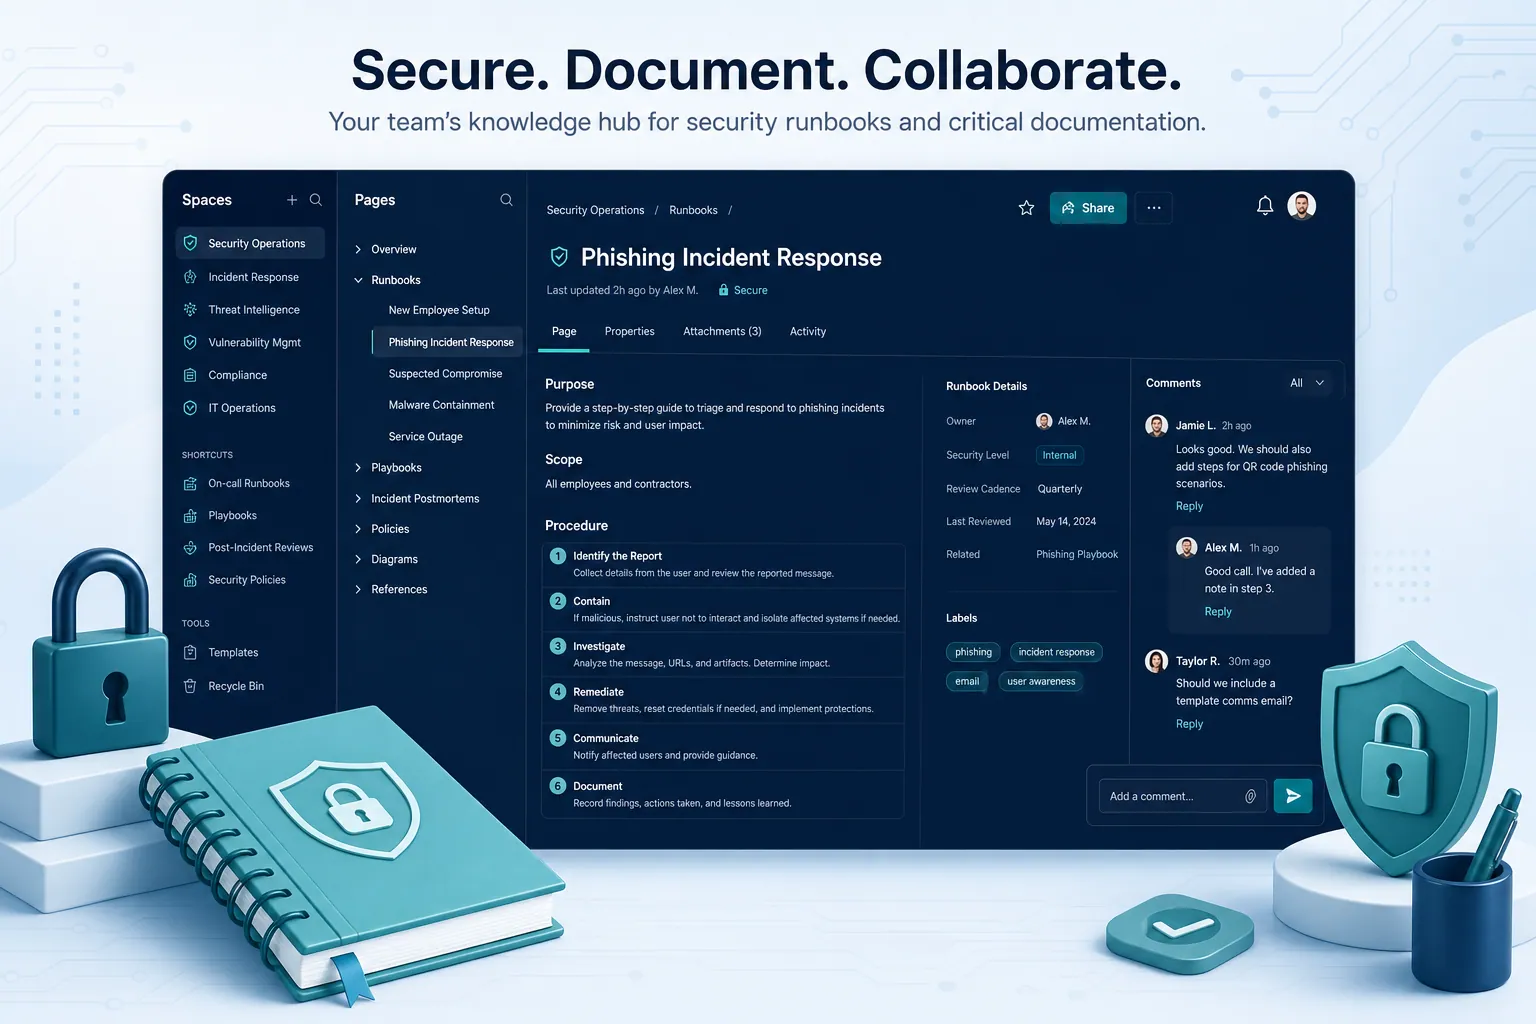
ZenXPages (Pages)
Structured docs your teams can publish, share, and keep current.
ZenXPages is Zenxsys’ live documentation workspace - spaces, collaborative editing, comments, and brand-consistent pages for runbooks, policies, and operational knowledge. Already available at pages.zenxsys.com.
- Structured publishing
- Team-ready workflows
- Comments & @mentions
ZenXPAM capabilities
Focused offerings grounded in what is actually built - not aspirational IAM suite filler.
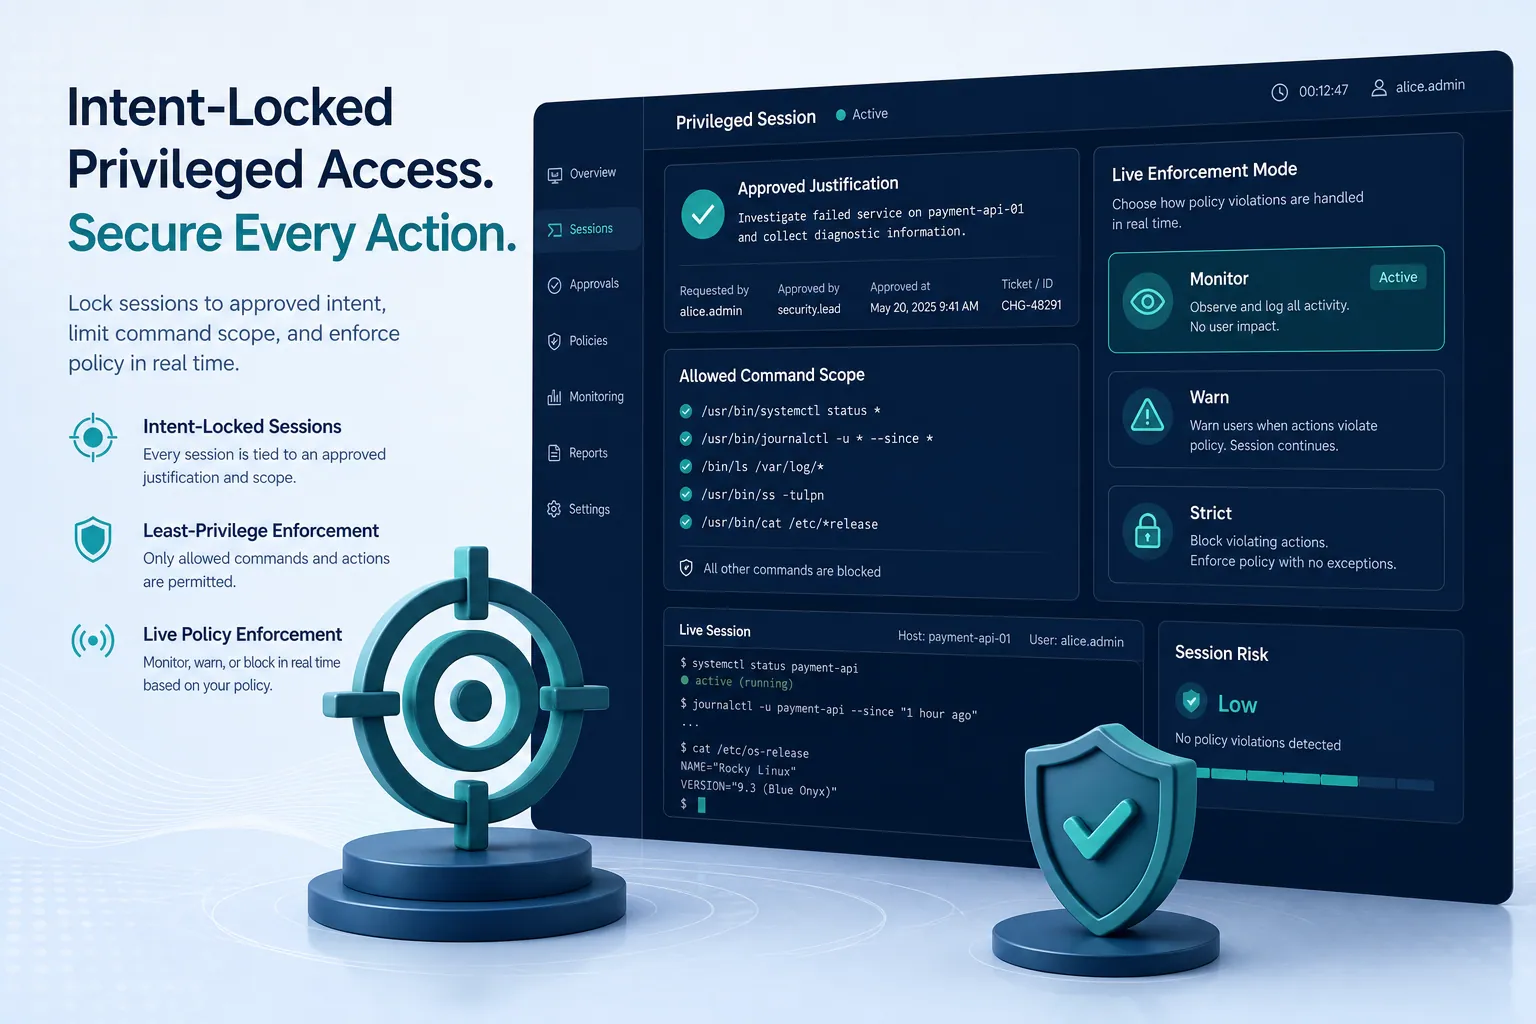
Intent-Locked Access
Access isn't just granted. It's held to what you said you'd do.
Every privileged session starts with a promise - "restart the DB after INC-4421," "patch the load balancer." Intent-Locked Access turns that promise into an enforceable boundary. The system reads the justification, compiles it into an approved scope, and watches the live session against it. Stray outside the scope and the session gets flagged, step-up challenged, or cut off - before damage happens, not after someone reviews the recording three weeks later.
- Justification → approved scope
- Live scoring against scope
- Monitor, Warn, Strict
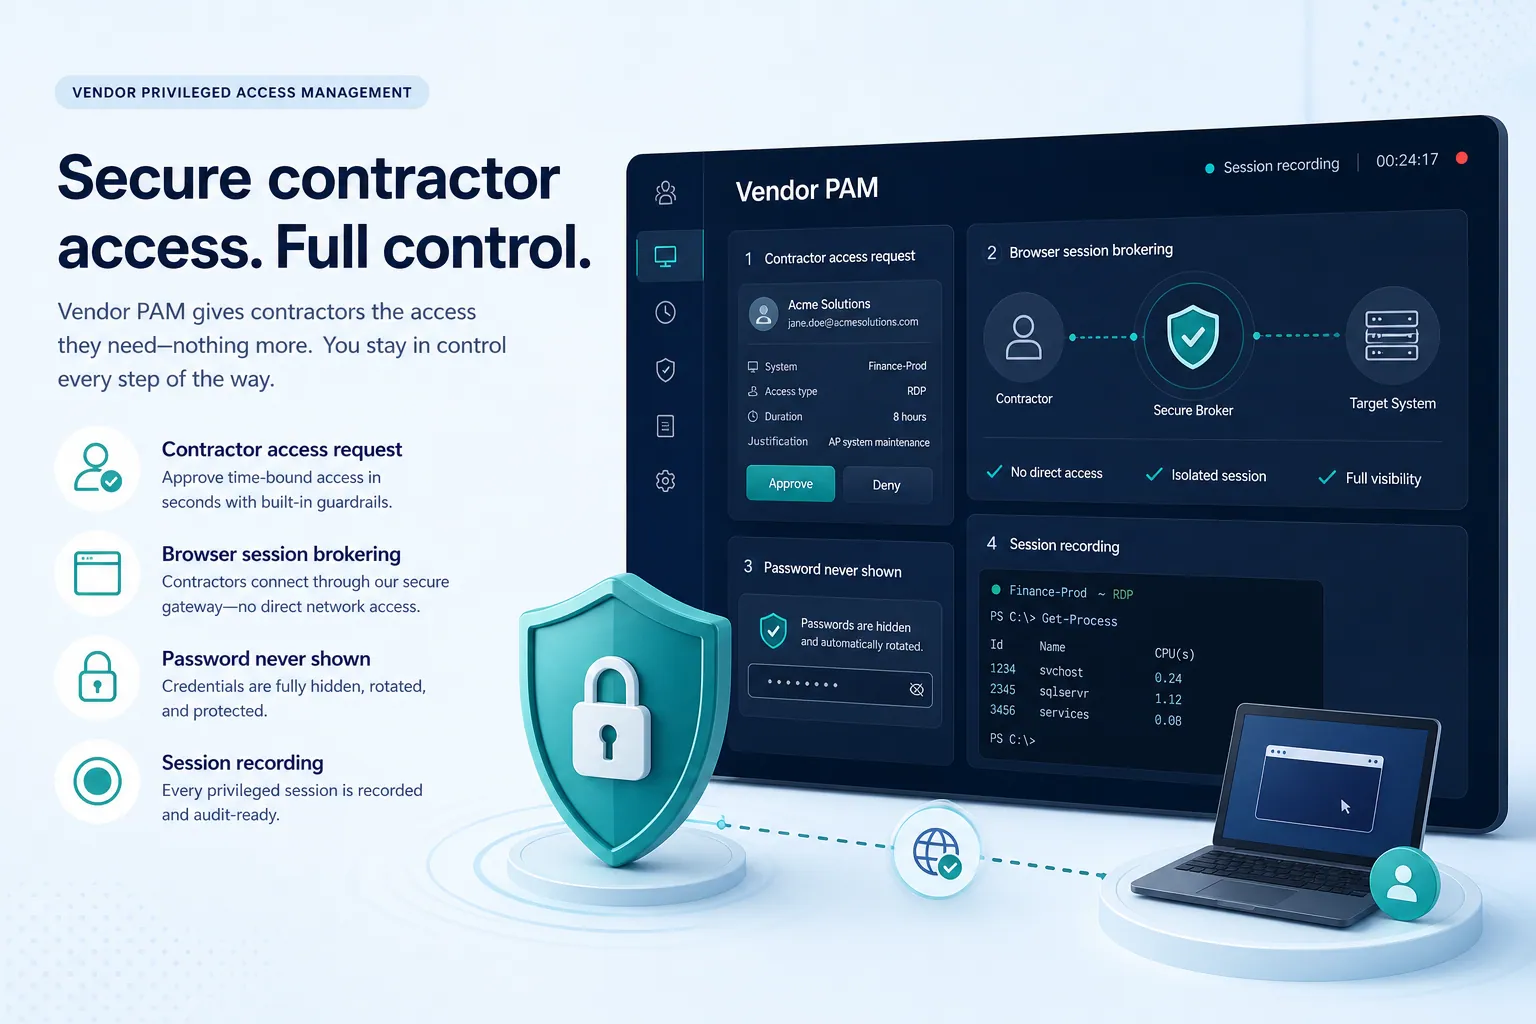
Vendor PAM
Give vendors access. Never give them the password.
Third-party access is where PAM programs quietly fail - vendors get VPN credentials, shared logins, standing accounts nobody remembers to revoke. Vendor PAM flips that: contractors and remote admins connect through the browser, the platform injects credentials server-side, and every session is recorded start to finish. The vendor never sees a password. You never lose visibility.
- Clientless RDP, SSH & web
- Server-side credential injection
- Searchable session playback
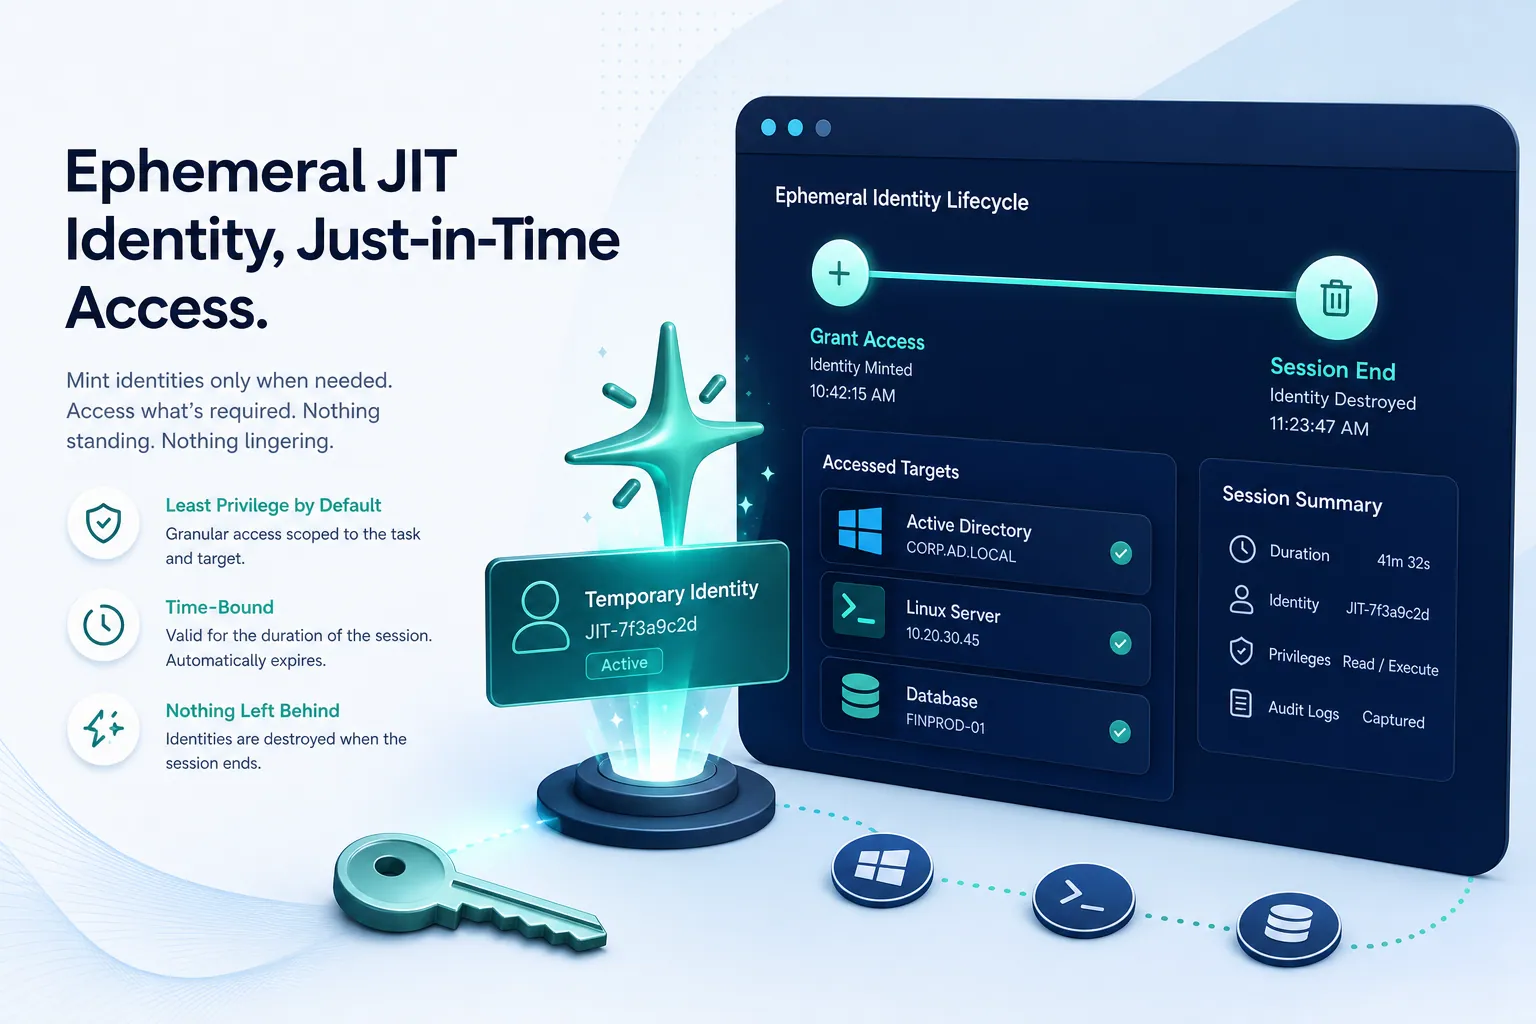
Ephemeral Identity
No account existed before the request. No account exists after it’s done.
Standing privileged accounts are the thing every breach report blames. Ephemeral Identity removes them from the equation - a real AD, Linux, or database account is minted the moment access is approved, and it’s gone the moment the session ends or the window expires. There’s nothing to rotate, nothing to forget, nothing sitting around waiting to be compromised.
- Real identities on grant
- Automatic deprovisioning
- Works on systems you have
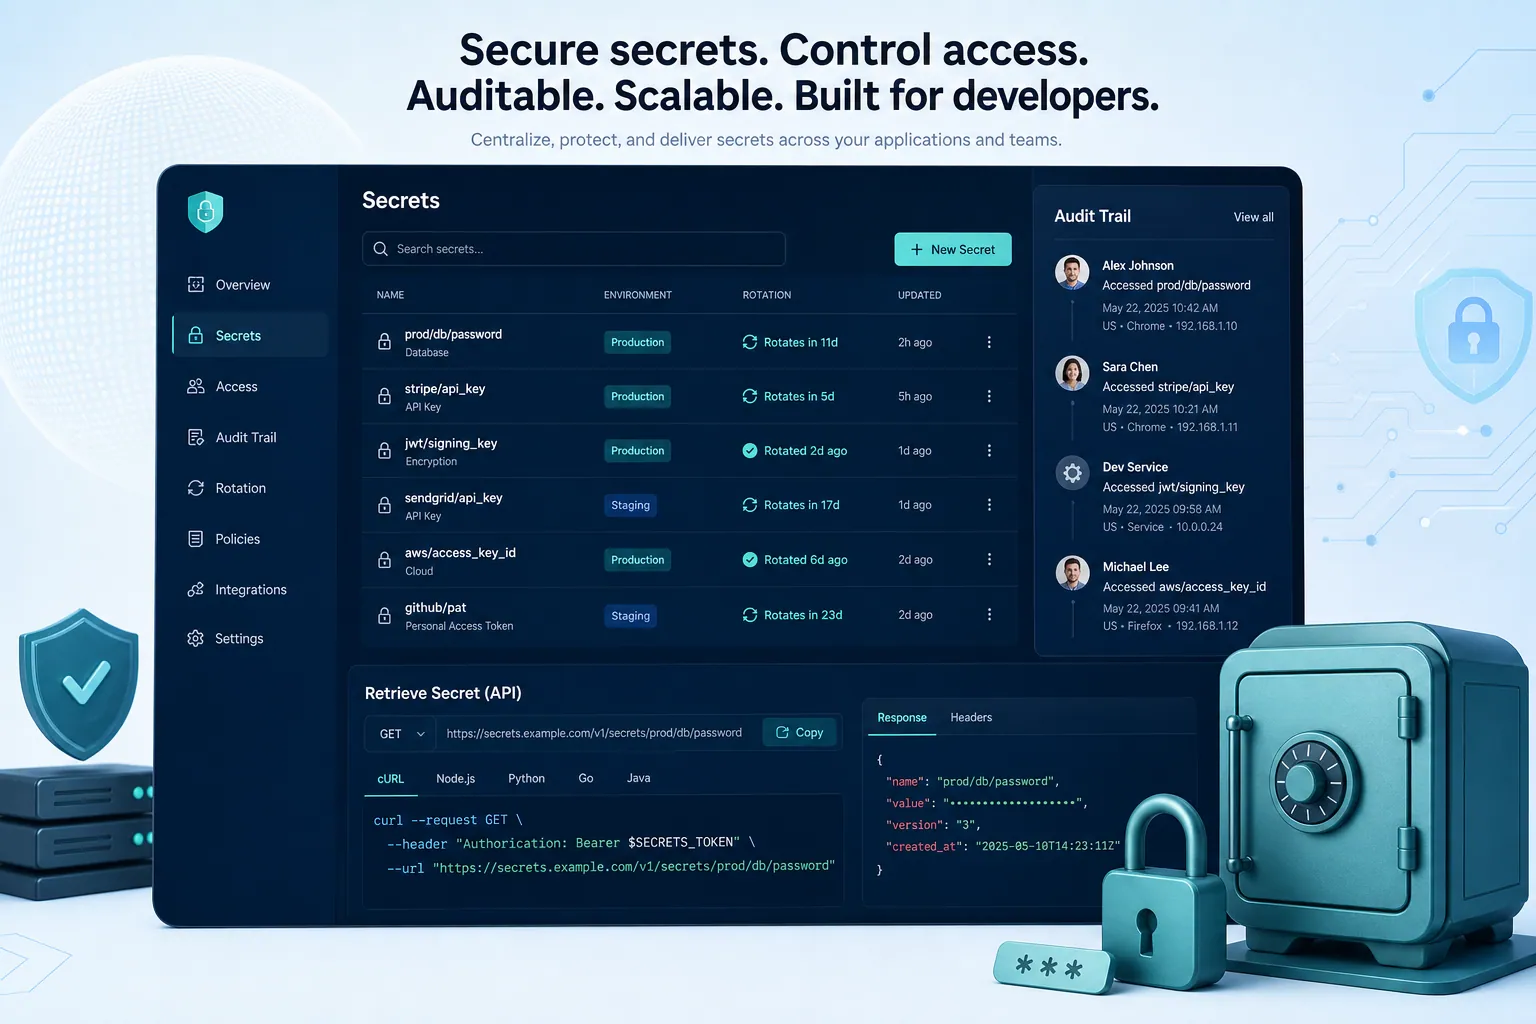
ZenxVault
One vault. Every secret. Nothing leaves your control.
Secrets sprawl because every team builds its own workaround - a `.env` file here, a shared password doc there, a script with a hardcoded key nobody wants to touch. ZenxVault gives every team one encrypted, audited place to store and retrieve secrets, with nothing routed through a third-party cloud unless you want it to be.
- AES-256 with your database
- Multi-tenant by design
- Full audit trail
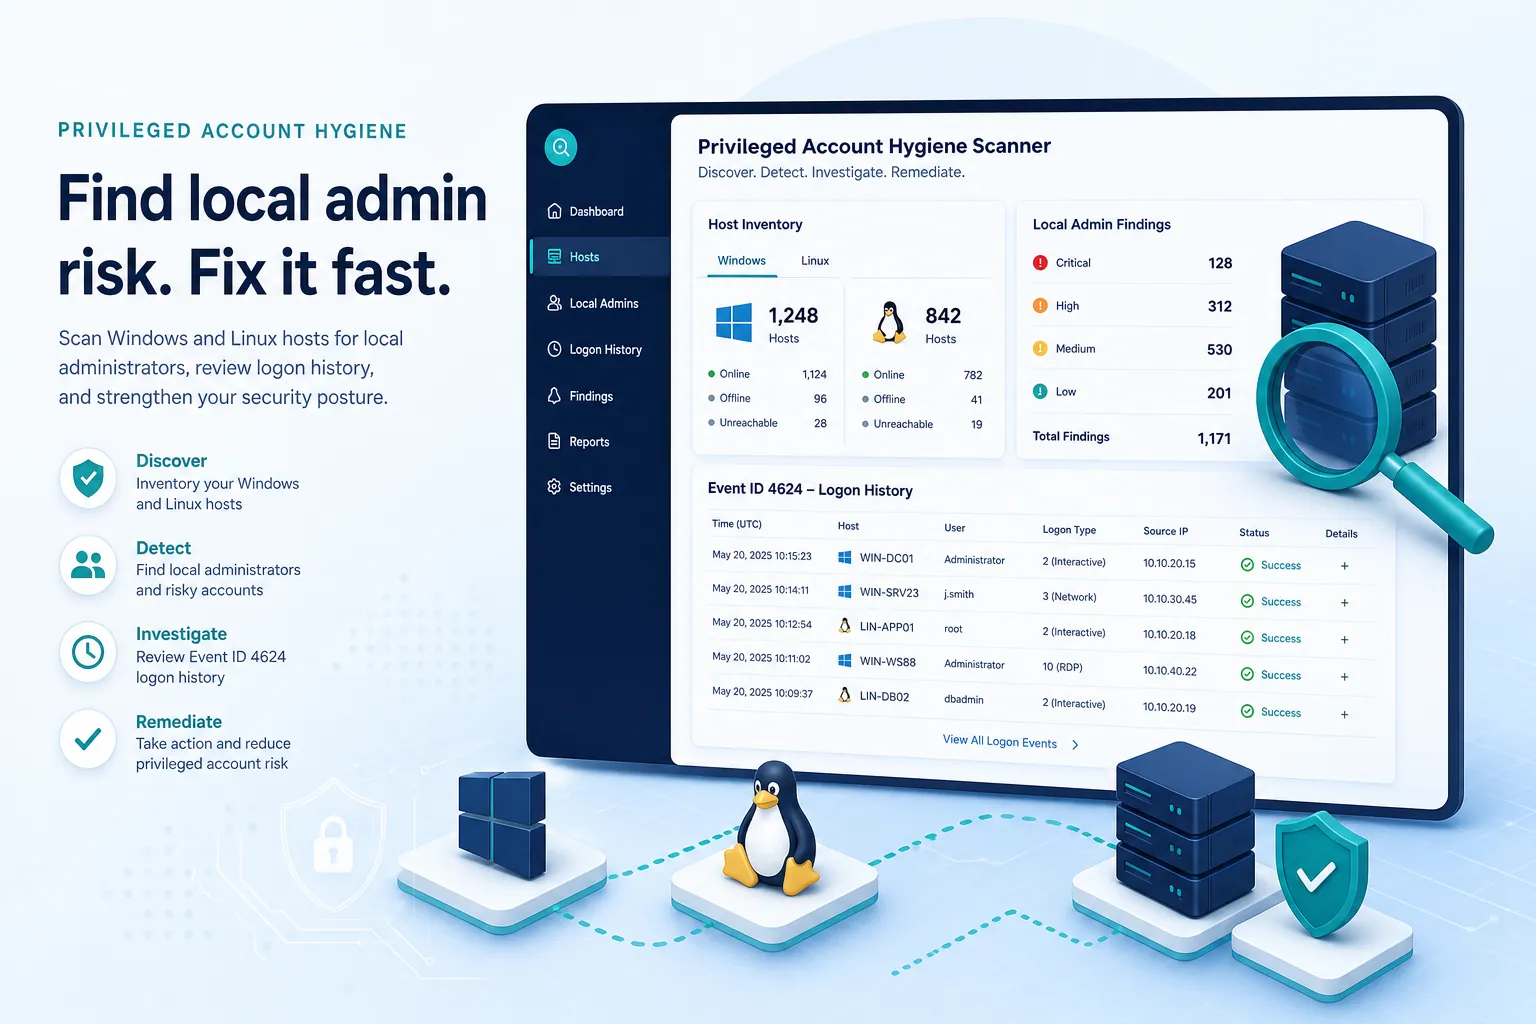
Privileged Account Hygiene Scanner
Find the admin accounts nobody remembers creating.
Every environment accumulates privilege it didn’t mean to keep - a local admin account from a project that ended two years ago, a service account with a password that’s never rotated, an install nobody approved. The Hygiene Scanner sweeps your estate over SSH and WinRM and surfaces exactly where standing privilege is hiding, without pretending to be a full endpoint management suite.
- Host inventory
- Windows logon history
- Works with partial credentials
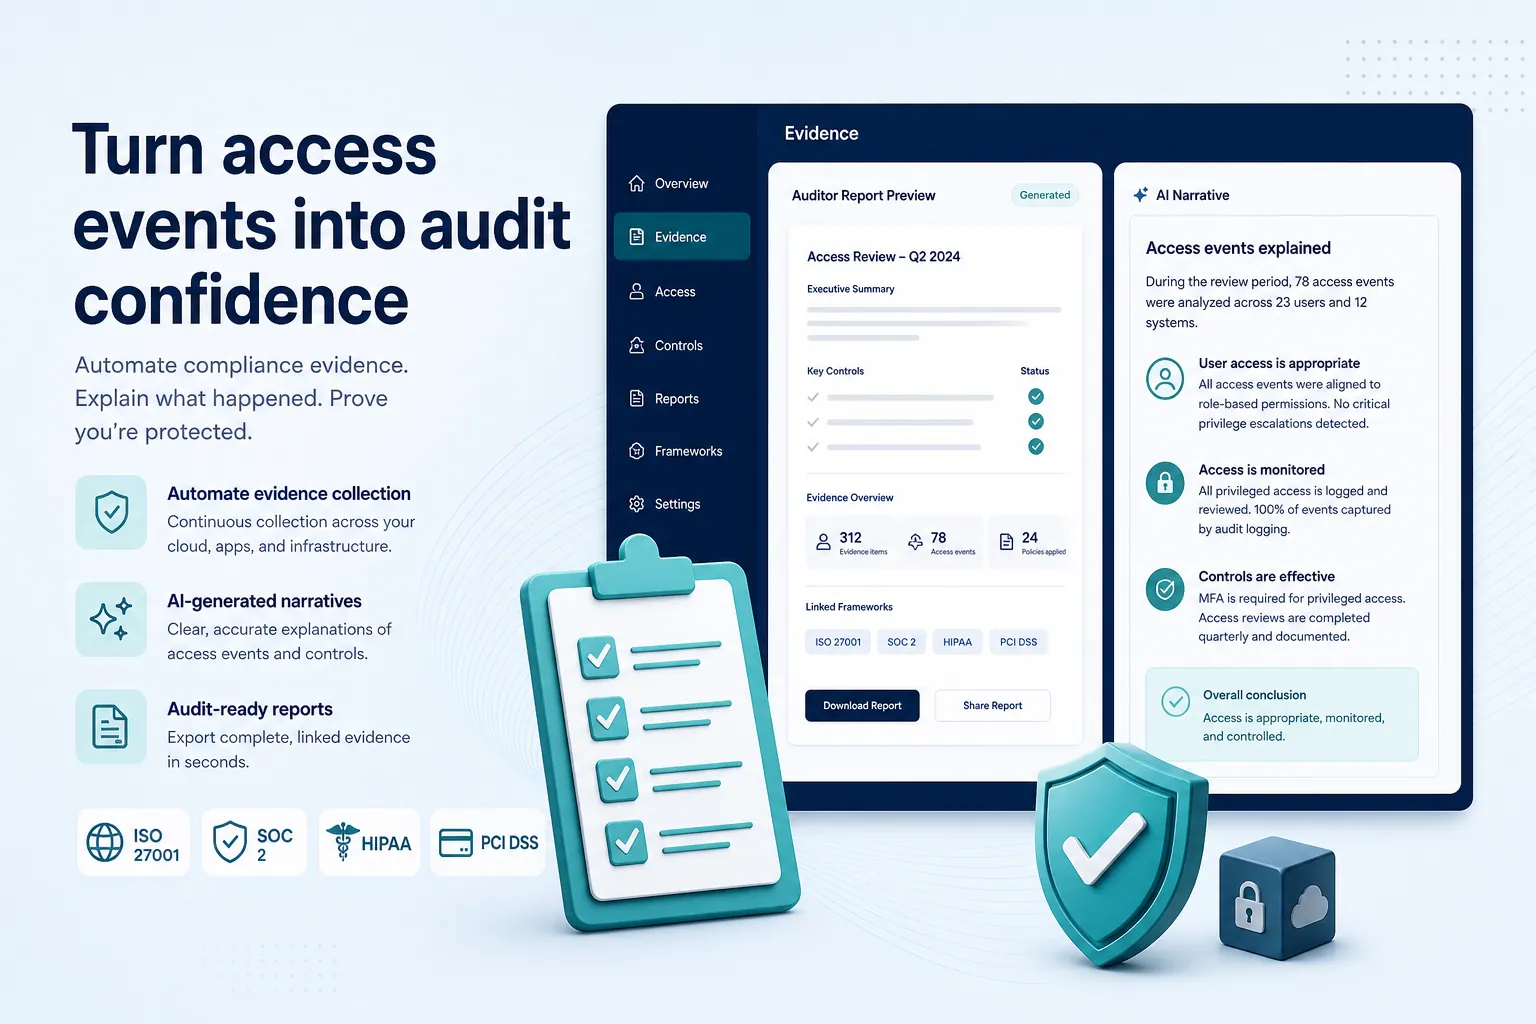
Compliance Evidence Automation
Audit-ready isn't a quarterly project anymore. It's just on.
Compliance evidence used to mean weeks of screenshots, spreadsheets, and Slack threads before an audit. Compliance Evidence Automation collects it continuously from every access event, generates plain-English narratives explaining what happened and why it satisfies the control, and hands your auditor a report instead of a scavenger hunt.
- Continuous evidence collection
- AI-generated narratives
- Searchable, tamper-evident trail
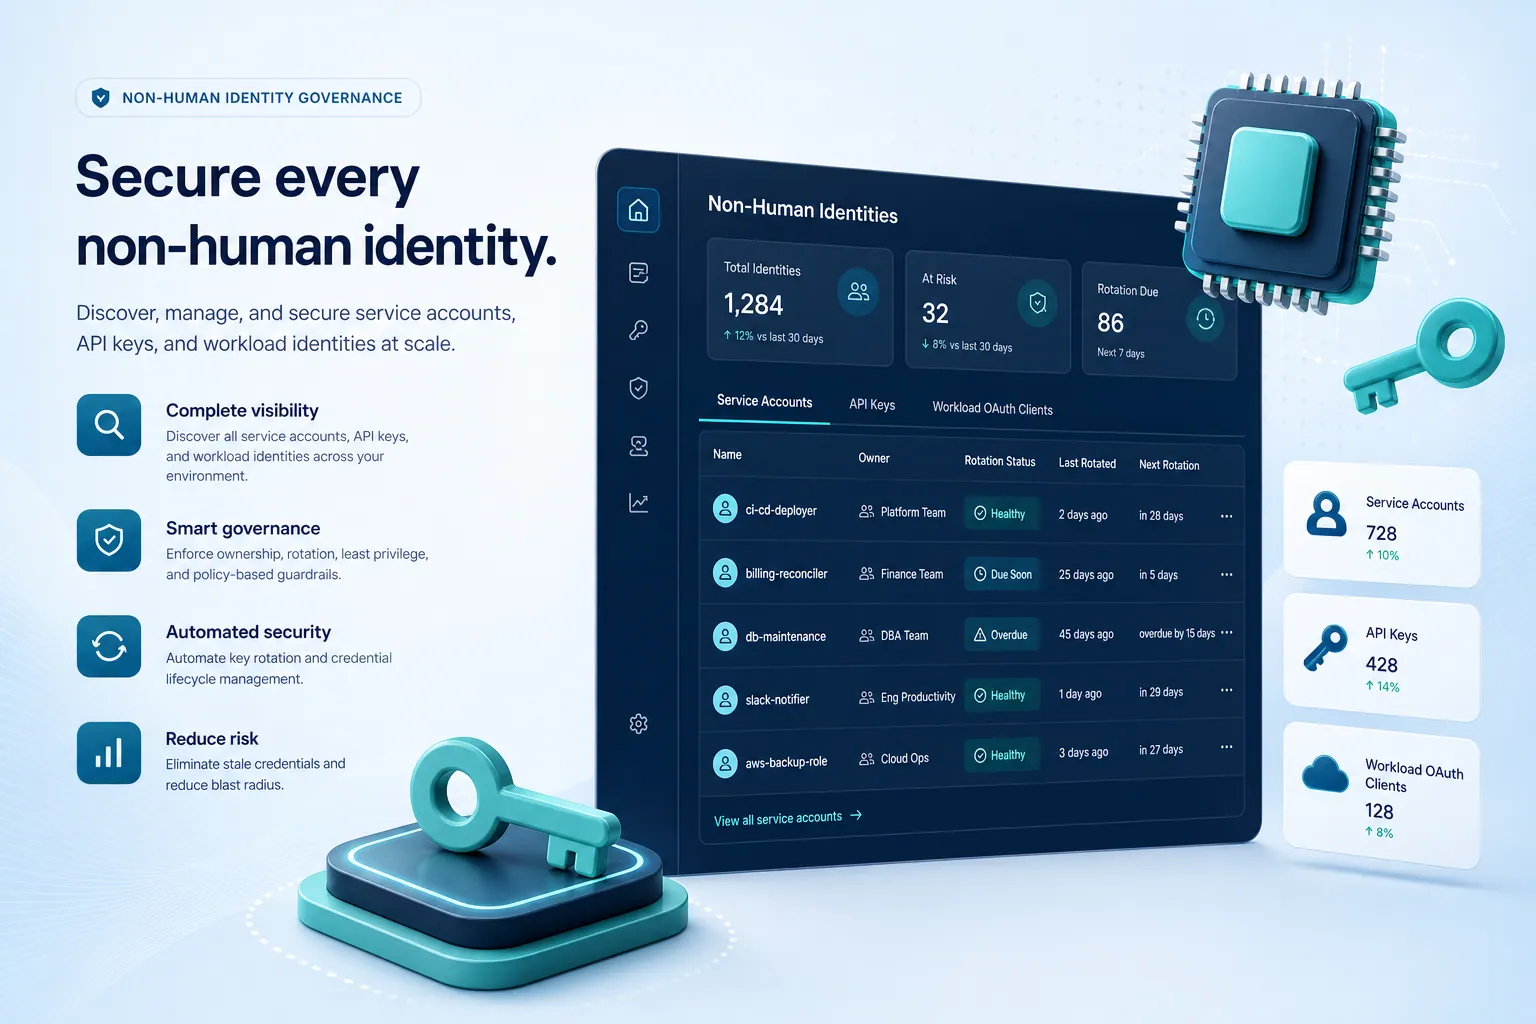
Non-Human Identity Governance
Your service accounts have more access than most of your employees. Time someone managed that.
Machine identities - service accounts, API keys, workload credentials - now outnumber human users in most enterprises, and almost nobody governs them the way they govern people. NHI Governance brings the same lifecycle discipline to machine identity that you already apply to human access: known ownership, credential rotation, and visibility into what every non-human identity can actually touch.
- AWS, Azure & GitHub connectors
- Centralized machine-identity visibility
- Lifecycle governance
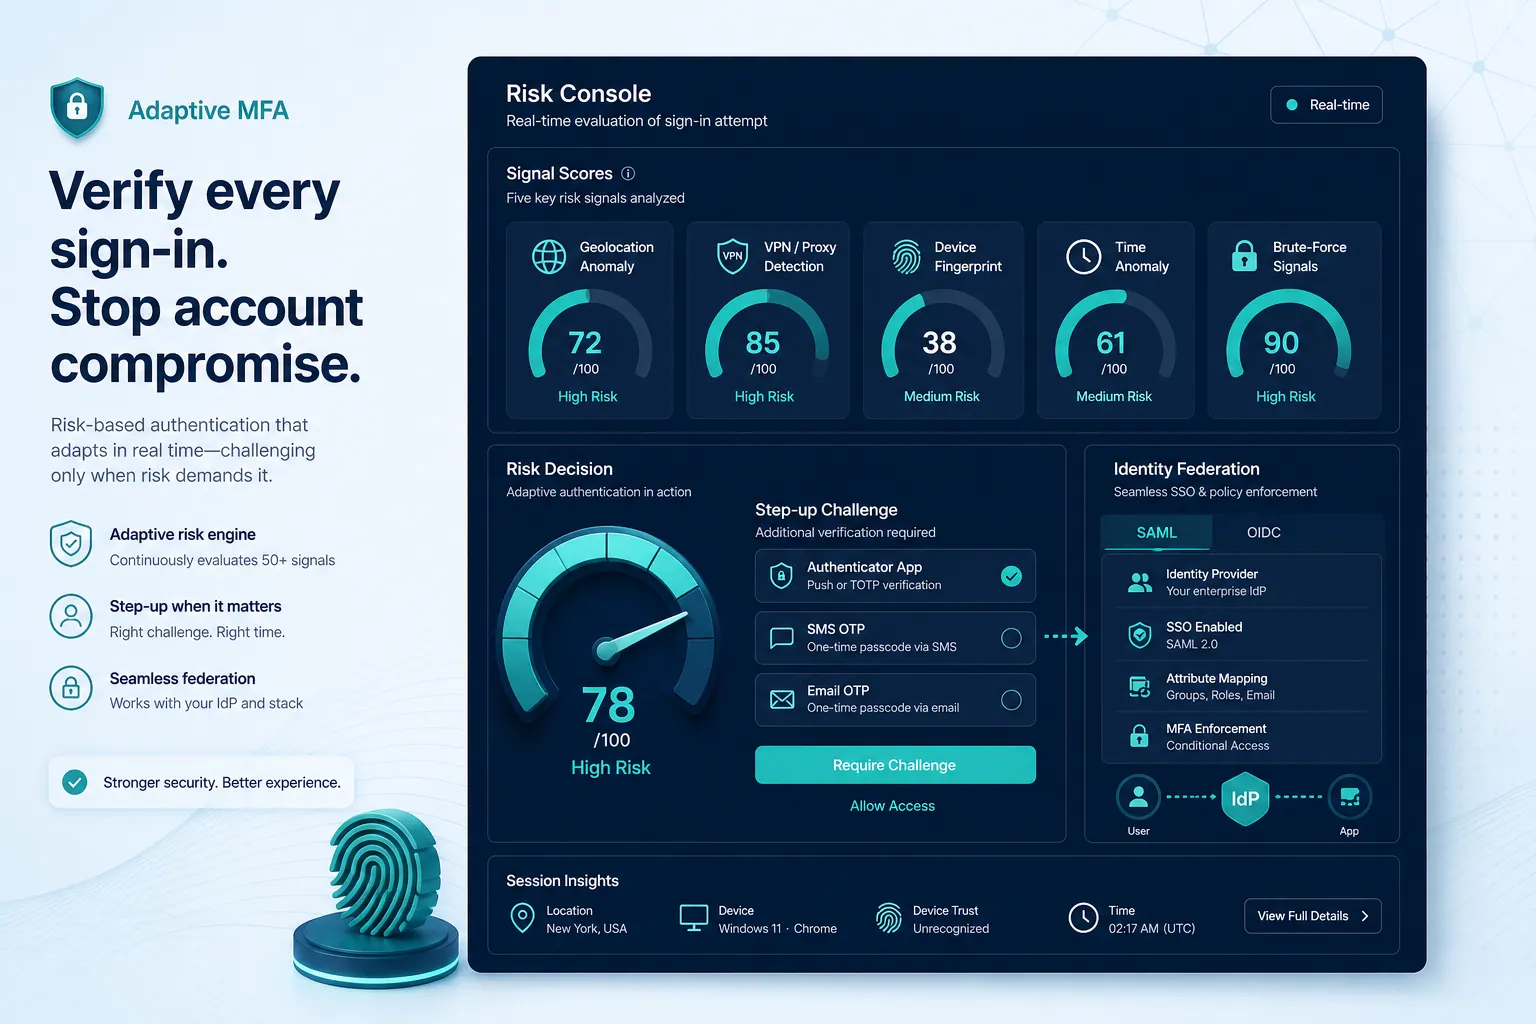
Adaptive Risk & Identity Federation
An explainable risk engine - and native SSO into the IdP you already run.
Adaptive MFA here is not a generic policy toggle. A real signal engine scores every login on geo-distance, VPN/Tor/proxy detection, device fingerprinting, time-of-day anomaly against user history, and brute-force behavioral scoring - then turns that into live step-up challenges. Alongside it: native SAML 2.0, OIDC, and LDAP federation so you plug into the identity provider your enterprise already trusts.
- Explainable risk scoring
- Live adaptive MFA step-up
- Native SAML 2.0 & OIDC
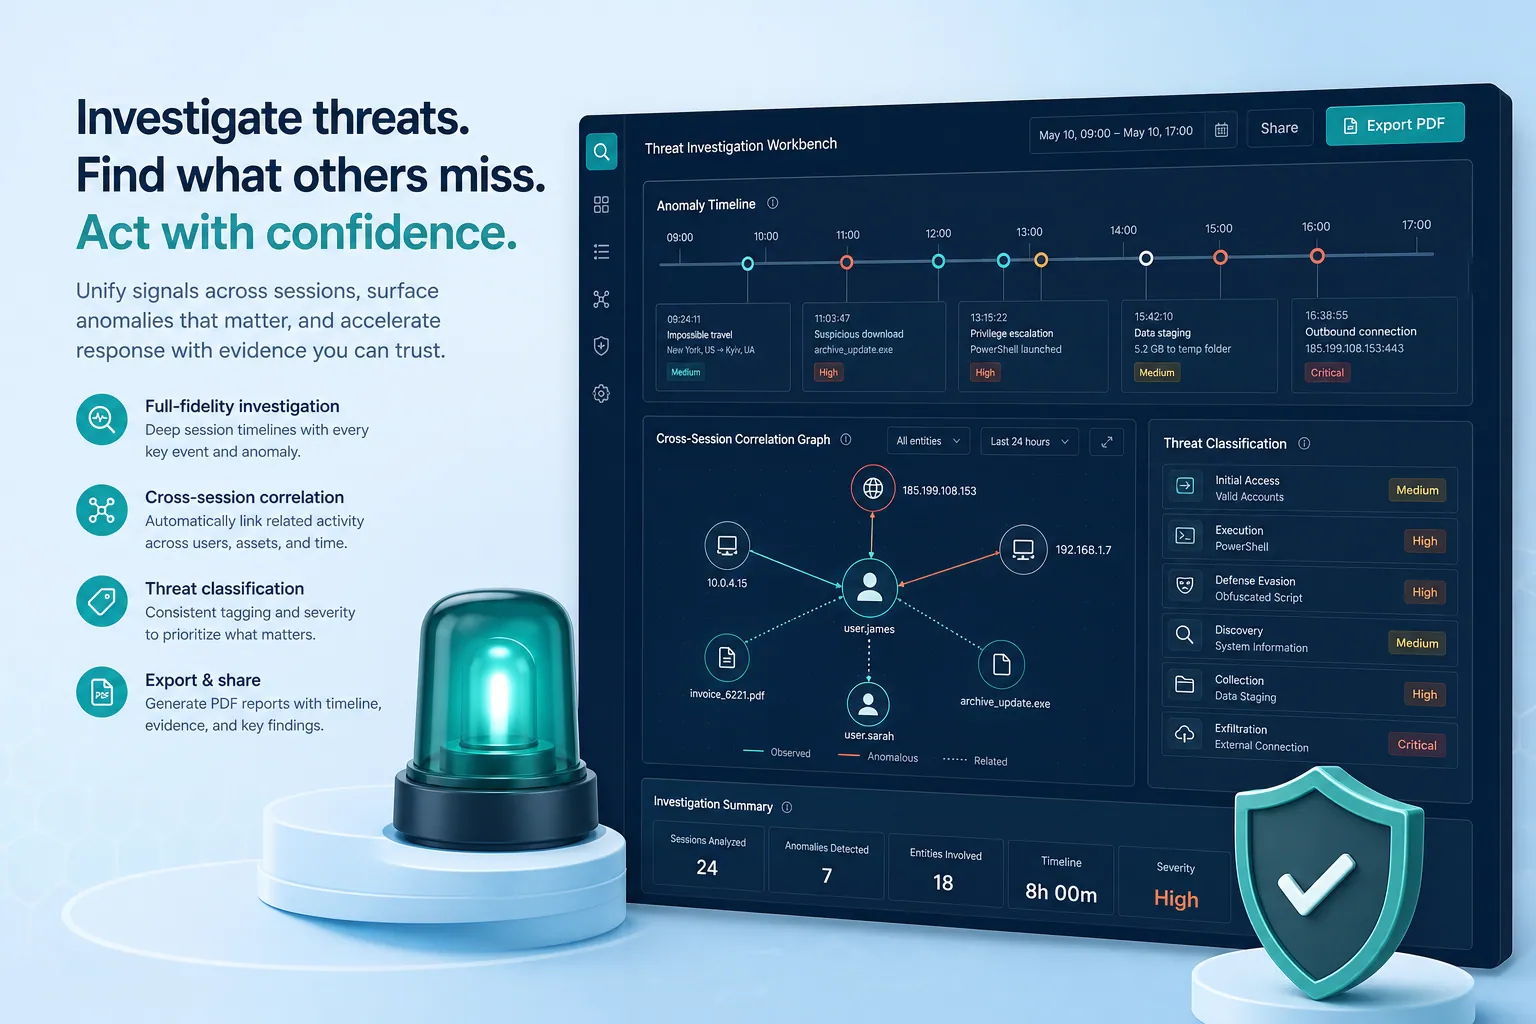
Threat Detection & Investigation
Detect anomalous behavior. Reconstruct what happened. Export the report.
Distinct from session recording. Behavior analysis, anomaly detection, threat classification, and cross-session event correlation feed a full investigation workbench - timeline reconstruction, pattern detection, and PDF report export. Recording watches. This detects and investigates.
- Behavior analysis & anomaly detection
- Cross-session correlation
- Investigation workbench
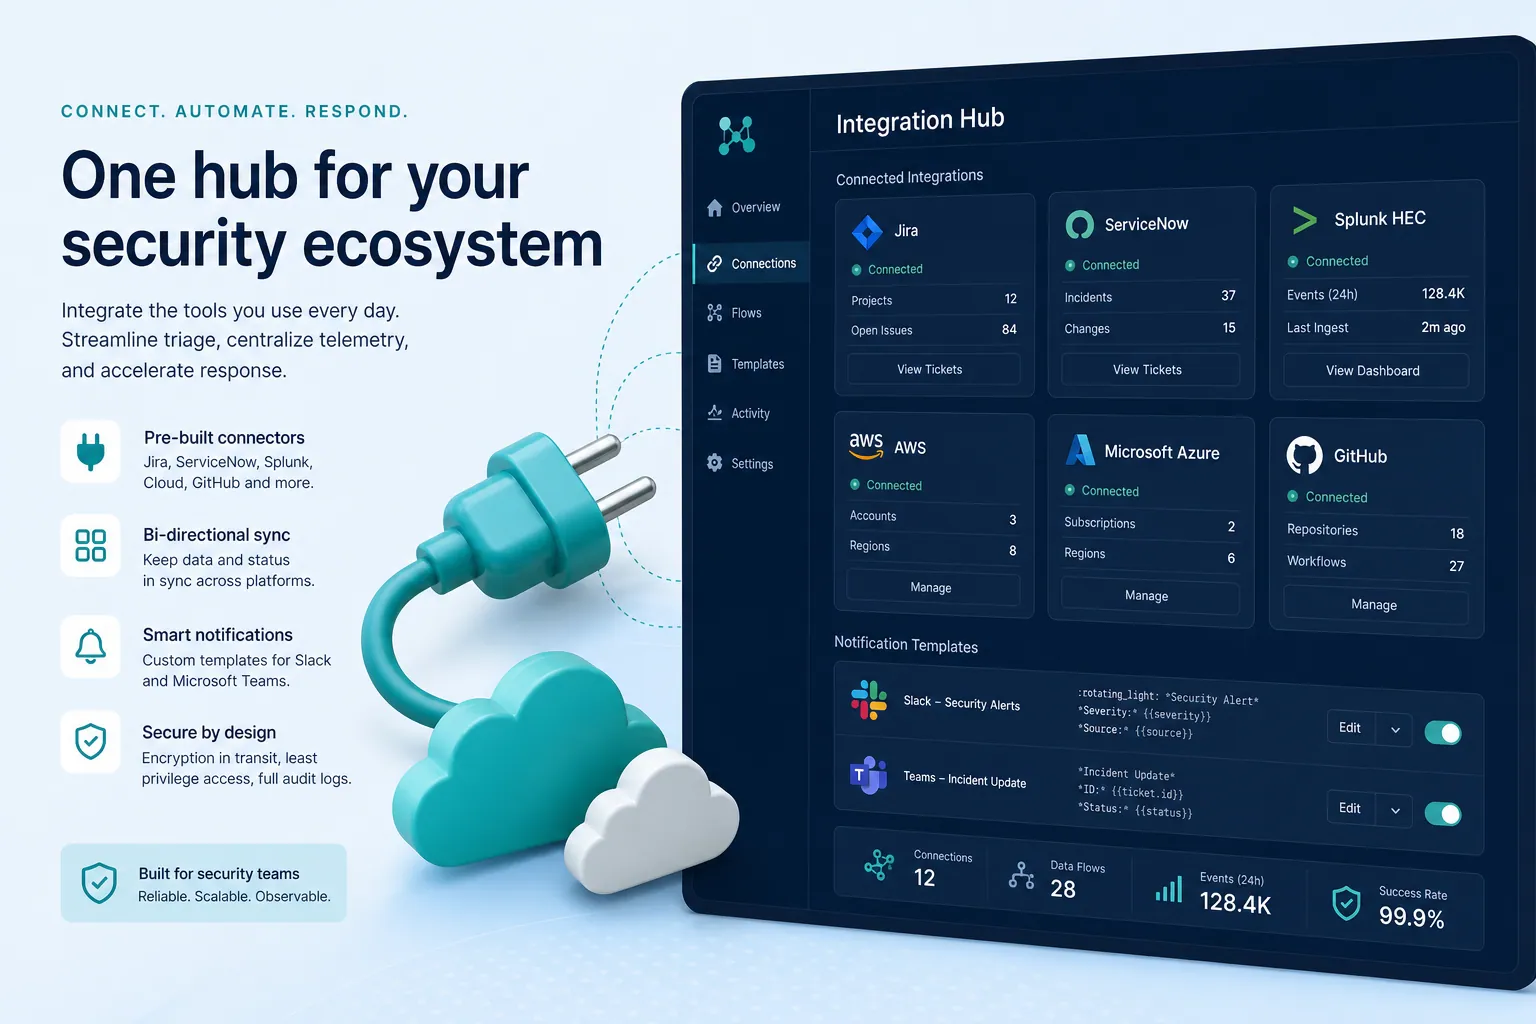
Integration Hub
ITSM, SIEM, and cloud connectors for the stack you already run.
Access requests sync with your change-management process. Security events feed the SIEM you already trust. Credentials connect to AWS, Azure, and GitHub with enterprise delivery resilience. Plus first-party notifications across SMS, email, Slack, Teams, and push - not a generic webhook dump.
- Bidirectional ITSM
- SIEM export in vendor formats
- Multi-cloud credential connectors
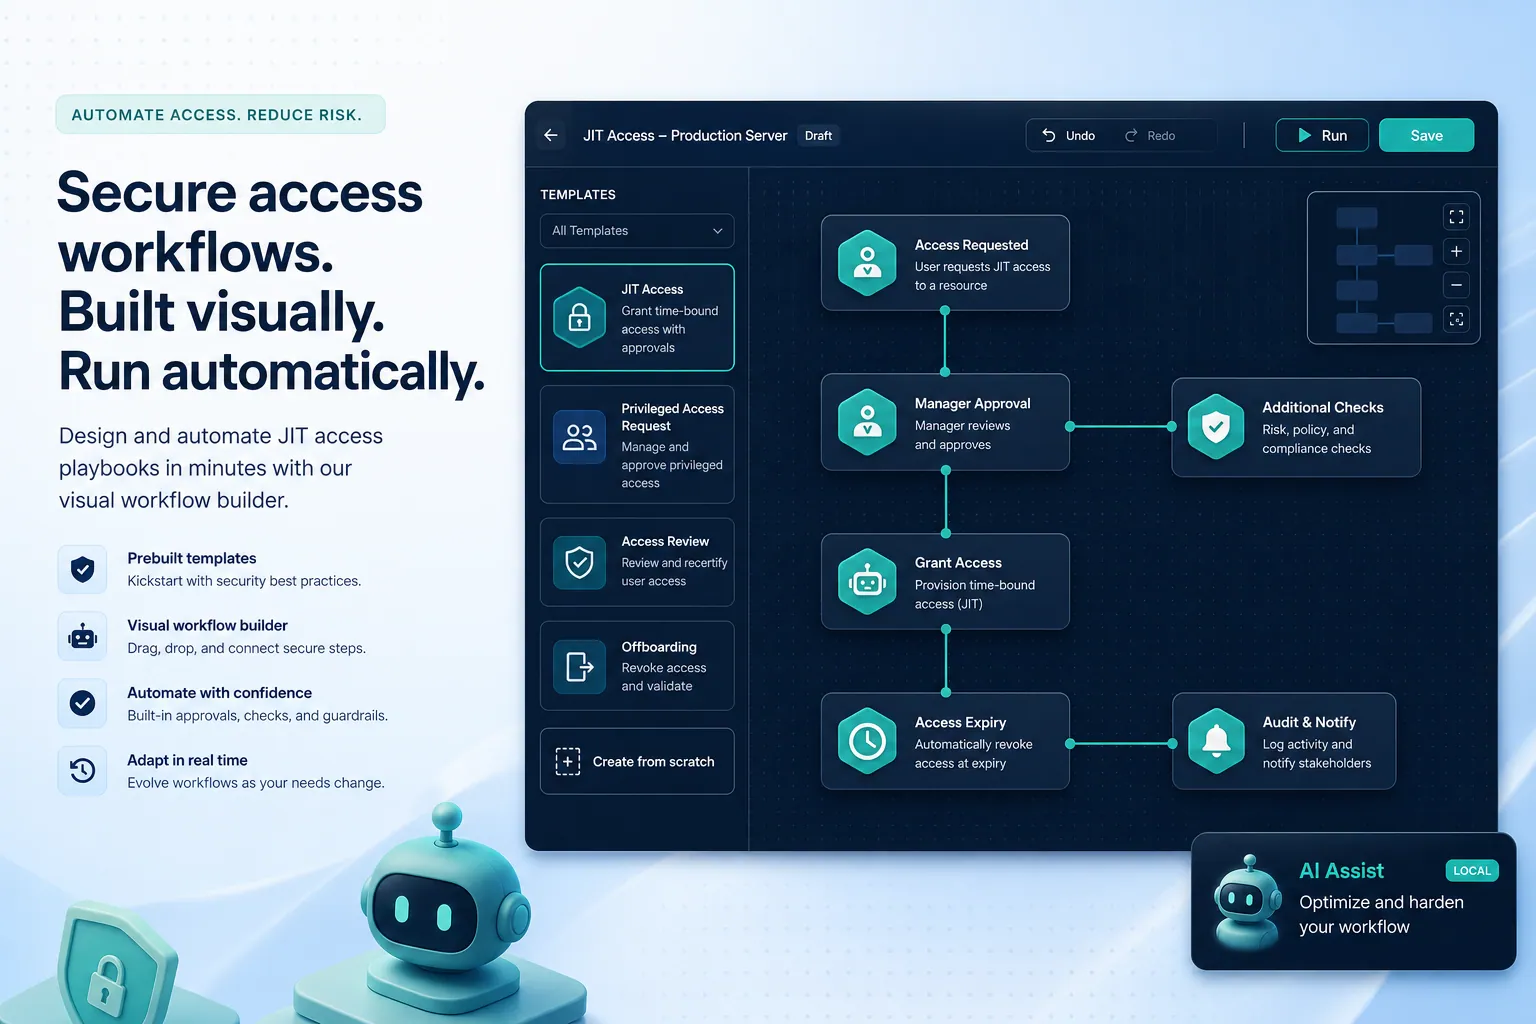
Workflow Automation
Drag-and-drop PAM playbooks - with optional local-AI assist, not AI theatre.
A full canvas automation builder - undo/redo, alignment, clipboard - with real execution behind it and 15+ prebuilt playbooks for JIT access, rotation, emergency access, threat response, onboarding/offboarding, access review, and MFA enrollment. Optional AI suggestions call local Ollama with a rule-based fallback, so automation still ships when Ollama is not available.
- Visual workflow canvas
- 15+ prebuilt PAM playbooks
- Optional local-AI assist
Why teams choose ZenXPAM
Local-first private AI
AI runs on local models inside your network - including task triage with priority, effort, confidence, and reasoning. Built for HIPAA, GDPR, and financial sovereignty.
Explainable adaptive risk
Five live login signals drive step-up MFA - geo, VPN/proxy, device, time anomaly, and brute-force behavior - with an admin Assessment Lab to prove the decision.
Integrates with what you run
Bidirectional Jira/ServiceNow, Splunk HEC and CEF/LEEF SIEM export, plus AWS, Azure, and GitHub credential connectors.
Agentless browser PAM
Launch privileged tools - RDP, SSH, VNC, web apps, and Kubernetes consoles - from the browser with auto-credential injection and full recording, no VPN thick client required.