Adaptive Risk & Identity Federation
An explainable risk engine - and native SSO into the IdP you already run.
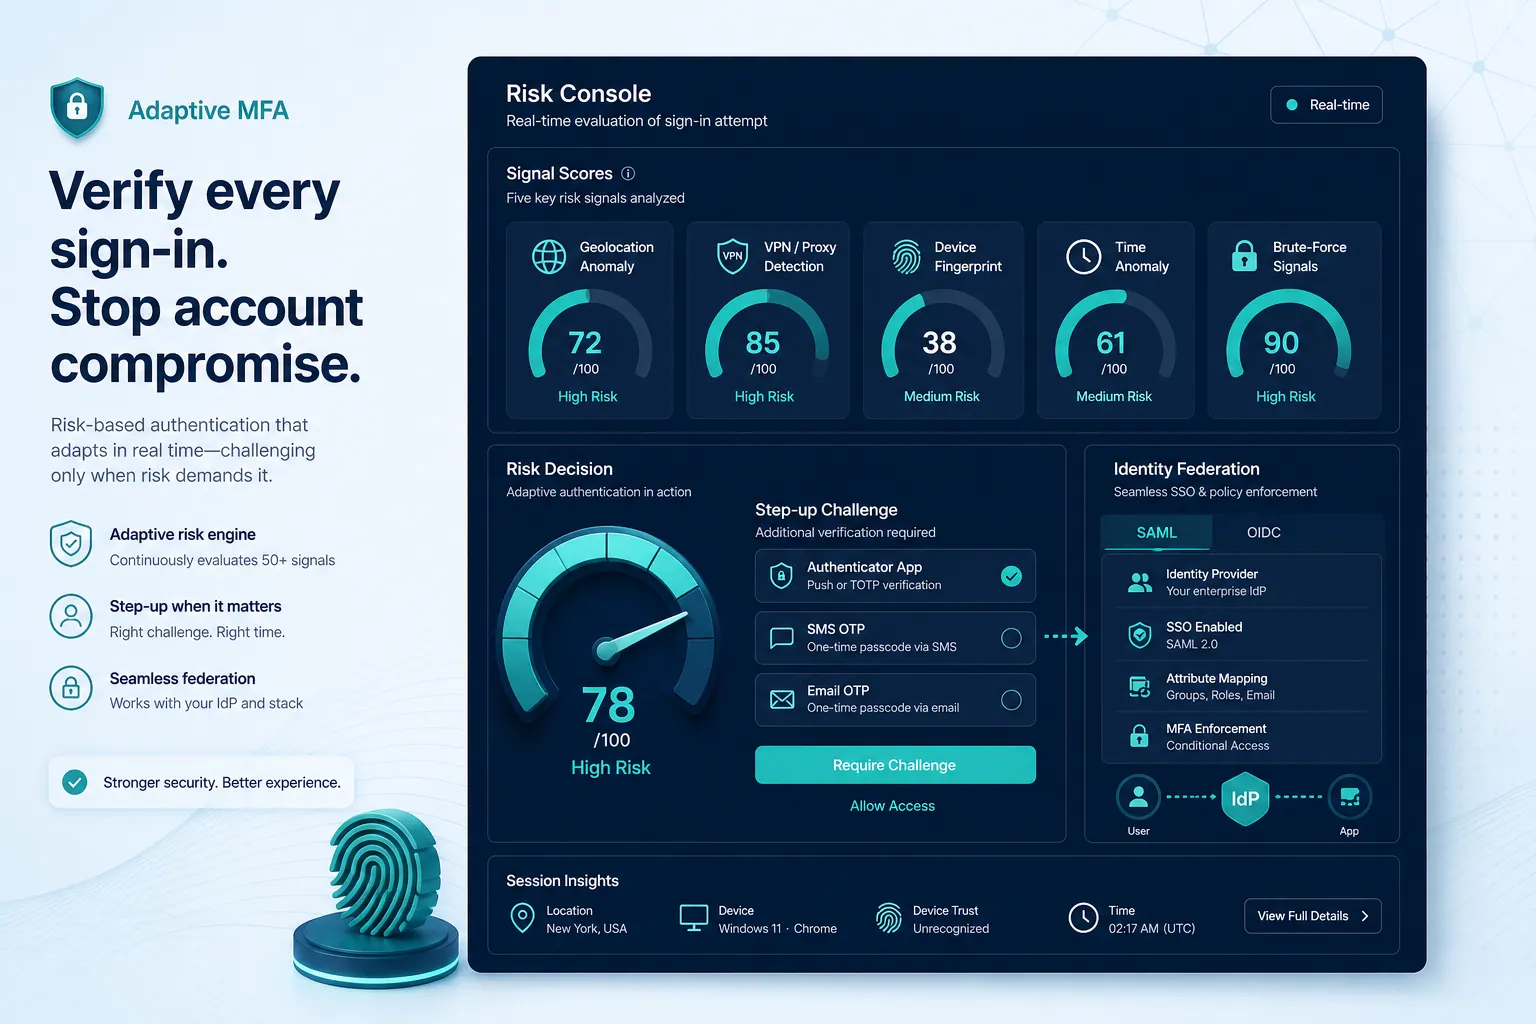
Adaptive MFA here is not a generic policy toggle. A real signal engine scores every login on geo-distance, VPN/Tor/proxy detection, device fingerprinting, time-of-day anomaly against user history, and brute-force behavioral scoring - then turns that into live step-up challenges. Alongside it: native SAML 2.0, OIDC, and LDAP federation so you plug into the identity provider your enterprise already trusts.
5
Live risk signals
Step-up
Challenges on risk
SAML
OIDC & LDAP native
Lab
Admin assessment sim
How it works
Explainable risk scoring
Five real signals - haversine geo-distance, VPN/Tor/proxy detection, device fingerprint, time-of-day anomaly vs. history, and brute-force behavioral scoring - not a black-box score.
Live adaptive MFA step-up
Risk decisions become step-up challenges in real time. Admins can use the Assessment Lab to simulate login context and watch the actual decision path.
Native SAML 2.0 & OIDC
Signed AuthnRequest XML, assertion validation, and OIDC federation - real protocol implementations, not a checkbox claim.
LDAP sync & provisioning
Real LDAP connections with incremental USN sync and bidirectional provisioning, managed from an Identity Providers admin experience.
Why it's different
Security buyers want to see under the hood. This is an explainable risk engine plus native federation into your existing IdP - two of the first questions on every RFP, answered with working protocol code.
Built for
Enterprises that already run Okta, Entra ID, AD, or LDAP and need step-up MFA they can defend in a security review.
- Explainable risk scoring
- Live adaptive MFA step-up
- Native SAML 2.0 & OIDC
- LDAP sync & provisioning