
Security & Availability · Supported
SOC 2 Type II
Service Organization Control 2 Type II
SOC 2 Type II
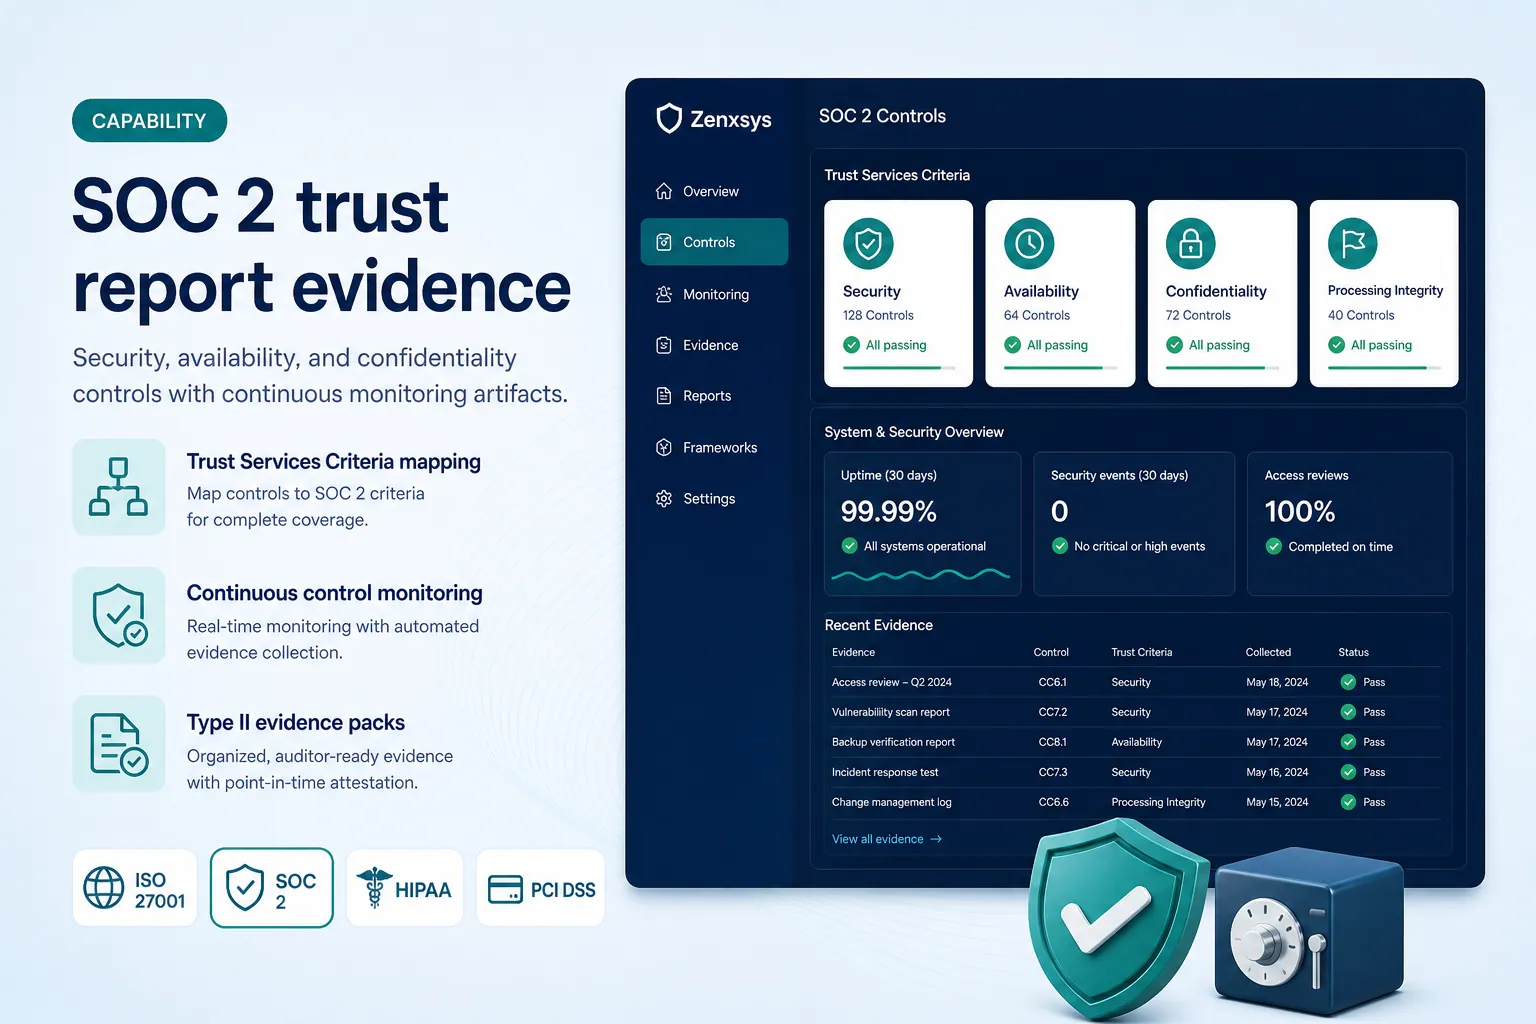
SOC 2 Type II examines whether controls operate effectively over a period, not just on paper. ZenXPAM seeds the framework, maps privileged access controls to named Trust Services Criteria such as CC6.7, and produces the dated, continuous evidence a Type II window needs. ZenXPAM does not hold a SOC 2 report of its own.
- Trust Services Criteria mapped clause by clause to internal controls
- Continuous automated checks that build evidence across the observation window
- Access certification campaigns evidencing periodic user access review
- Hash-chained audit of every privileged request, approval, and session
What is SOC 2 Type II?
SOC 2 Type II is a comprehensive auditing procedure that ensures service providers securely manage data to protect the interests and privacy of their clients. Developed by the American Institute of CPAs (AICPA), SOC 2 reports focus on a service organization's non-financial reporting controls related to security, availability, processing integrity, confidentiality, and privacy. Unlike SOC 2 Type I, which evaluates the design of controls at a specific point in time, Type II examines the operational effectiveness of controls over a period of time (typically 6-12 months). This certification demonstrates that an organization has not only designed appropriate controls but also effectively operates them consistently.
Where is SOC 2 Type II applicable?
SOC 2 Type II is primarily applicable to technology and cloud computing companies that store customer data in the cloud, including Software as a Service (SaaS) providers, data hosting companies, managed IT service providers, and any organization that processes, stores, or transmits customer data. It is especially important for B2B service providers who need to demonstrate their security posture to enterprise clients. Many enterprise customers require SOC 2 Type II certification before engaging with service providers, making it essential for companies serving large organizations. It's also relevant for financial services, healthcare technology, and any industry where data security and availability are critical business requirements.
Features, benefits & risks
Key Features
- Trust Services Criteria mapped clause by clause to internal controls
- Continuous automated checks that build evidence across the observation window
- Access certification campaigns evidencing periodic user access review
- Hash-chained audit of every privileged request, approval, and session
- Signed evidence packs with an offline verifier for your service auditor
Benefits
- Evidence generated continuously instead of assembled at year end
- Covers the logical access criteria auditors test hardest
- Gives your service auditor independently verifiable artefacts
- Reduces sampling effort across the observation period
- Supports customer security questionnaires with real control data
Risks
- Loss of enterprise customers who require SOC 2 certification
- Security incidents exposing customer data and trust
- Operational failures affecting service availability
- Compliance gaps leading to audit failures
- Competitive disadvantage in B2B markets