Ephemeral Identity
No account existed before the request. No account exists after it’s done.
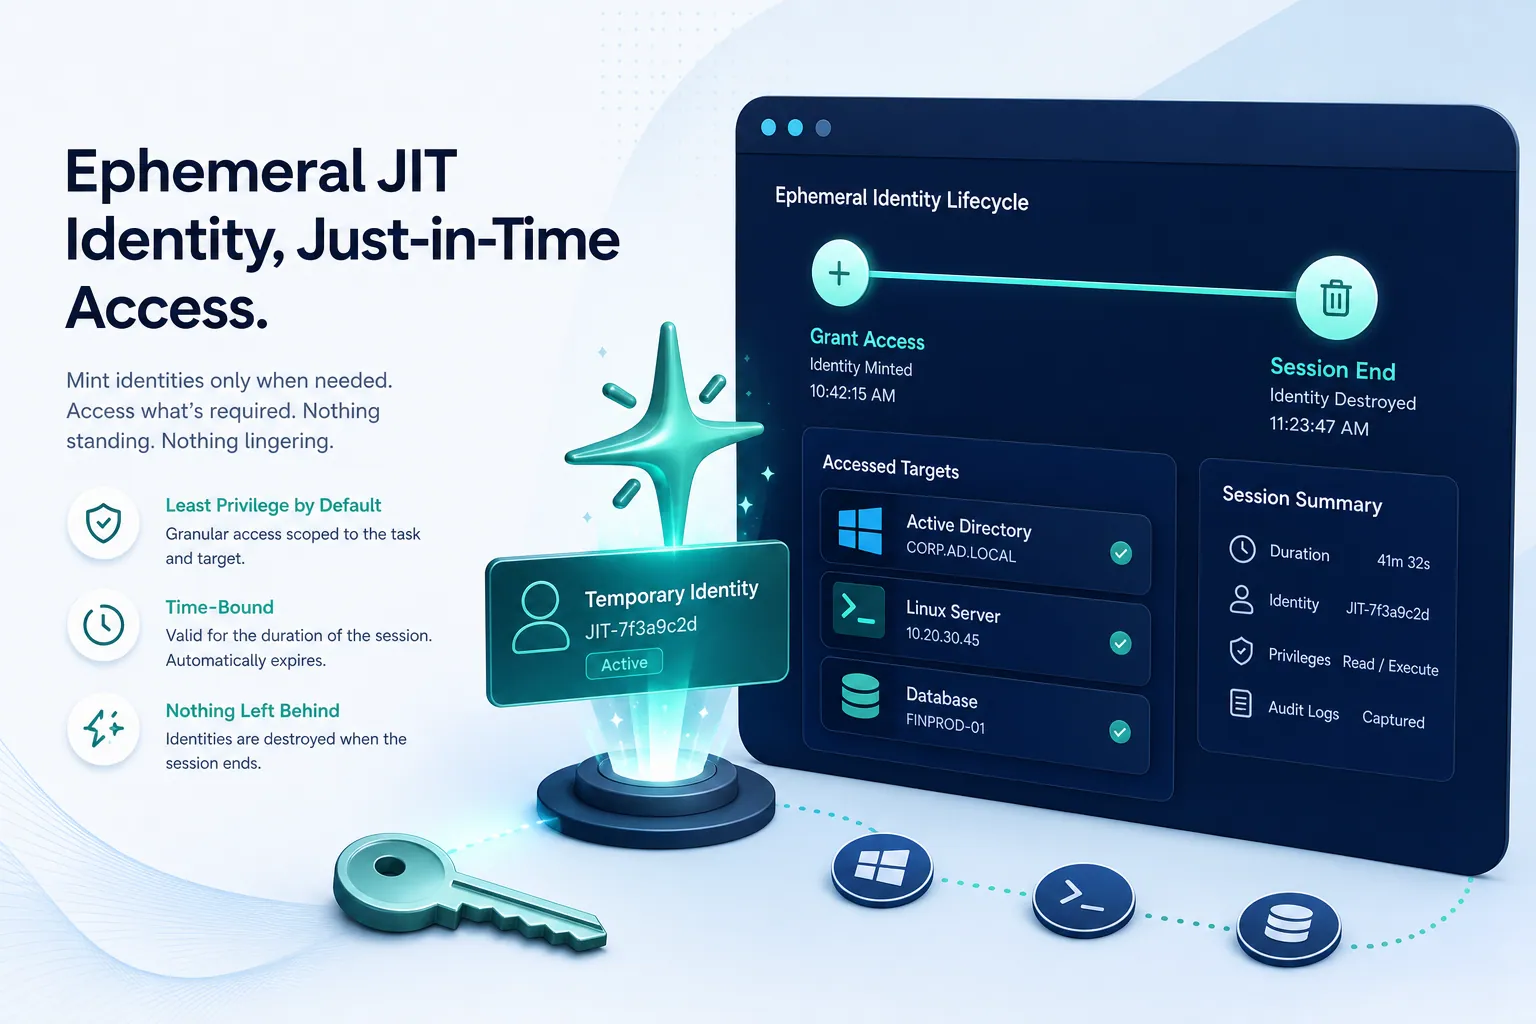
Standing privileged accounts are the thing every breach report blames. Ephemeral Identity removes them from the equation - a real AD, Linux, or database account is minted the moment access is approved, and it’s gone the moment the session ends or the window expires. There’s nothing to rotate, nothing to forget, nothing sitting around waiting to be compromised.
Mint
On grant
Gone
On revoke / expiry
AD+
Linux & databases
Fail
Closed on error
How it works
Real identities on grant
Functioning identities provisioned on approval - not shared logins, not vaulted passwords checked out and back in.
Automatic deprovisioning
Removed on revoke, session end, or access-window expiry - no manual cleanup step to skip.
Works on systems you have
Active Directory, Linux hosts, and databases - not just cloud-native infrastructure.
Fail-closed option
If provisioning fails, access simply doesn’t happen - no silent fallback to a standing account.
Why it's different
Ephemeral-credential access is common for cloud-native infrastructure. It’s rare for the legacy AD and Linux estate most enterprises still run on. This brings that model to the systems that actually need it most.
Built for
Security teams ready to say "we have zero standing privileged accounts" and mean it.
- Real identities on grant
- Automatic deprovisioning
- Works on systems you have
- Fail-closed option