Intent-Locked Access
Access isn't just granted. It's held to what you said you'd do.
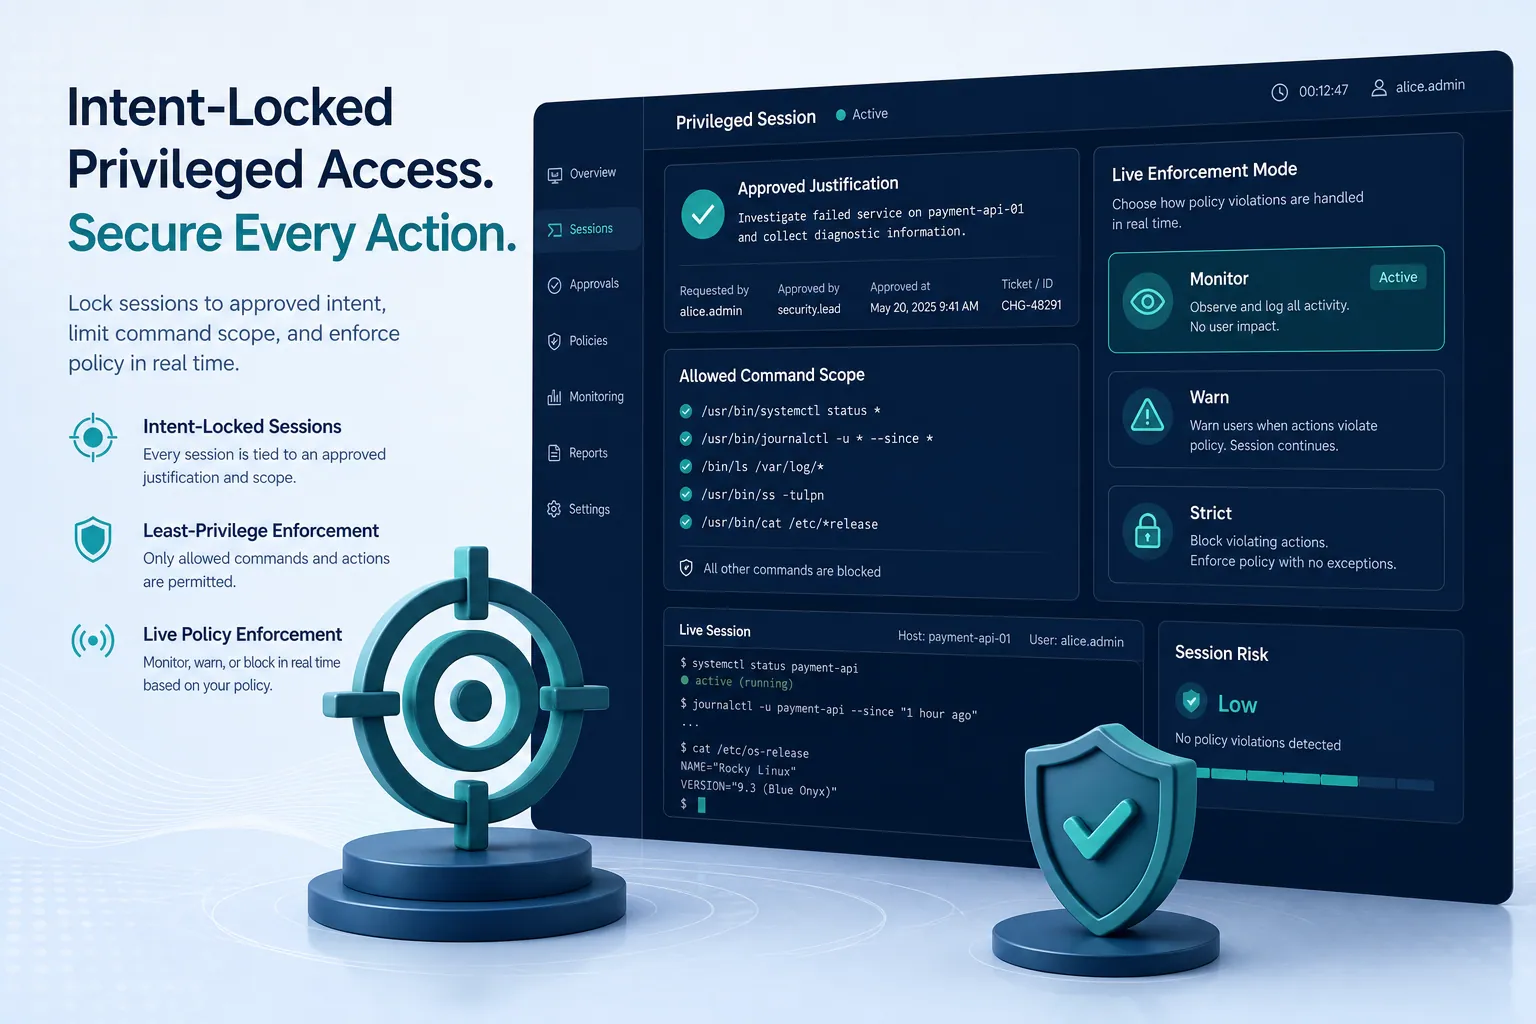
Every privileged session starts with a promise - "restart the DB after INC-4421," "patch the load balancer." Intent-Locked Access turns that promise into an enforceable boundary. The system reads the justification, compiles it into an approved scope, and watches the live session against it. Stray outside the scope and the session gets flagged, step-up challenged, or cut off - before damage happens, not after someone reviews the recording three weeks later.
Live
Scope enforcement
3
Enforcement modes
MFA
Step-up on deviation
Real-time
Not post-hoc review
How it works
Justification → approved scope
Plain-English justification compiled into an allowed command scope, reviewed and editable by the approver before access is granted.
Live scoring against scope
Session activity scored against that scope in real time - not just logged for later SIEM review.
Monitor, Warn, Strict
Three enforcement modes so you can roll it out without breaking workflows on day one.
Deviation response
Deviation triggers step-up MFA or session termination, matched to how far outside the scope the activity falls.
Why it's different
Most access tools stop at the approval. This one keeps enforcing the approval for the entire life of the session - the difference between a lock on the door and a guard who actually reads the guest list.
Built for
Security teams who are tired of finding out what happened after the incident, not during it.
- Justification → approved scope
- Live scoring against scope
- Monitor, Warn, Strict
- Deviation response