ZenxVault
One vault. Every secret. Nothing leaves your control.
Secrets sprawl because every team builds its own workaround - a `.env` file here, a shared password doc there, a script with a hardcoded key nobody wants to touch. ZenxVault gives every team one encrypted, audited place to store and retrieve secrets, with nothing routed through a third-party cloud unless you want it to be.
AES-256
Encryption
Self
Hosted control
Multi
Tenant ready
API
First design
How it works
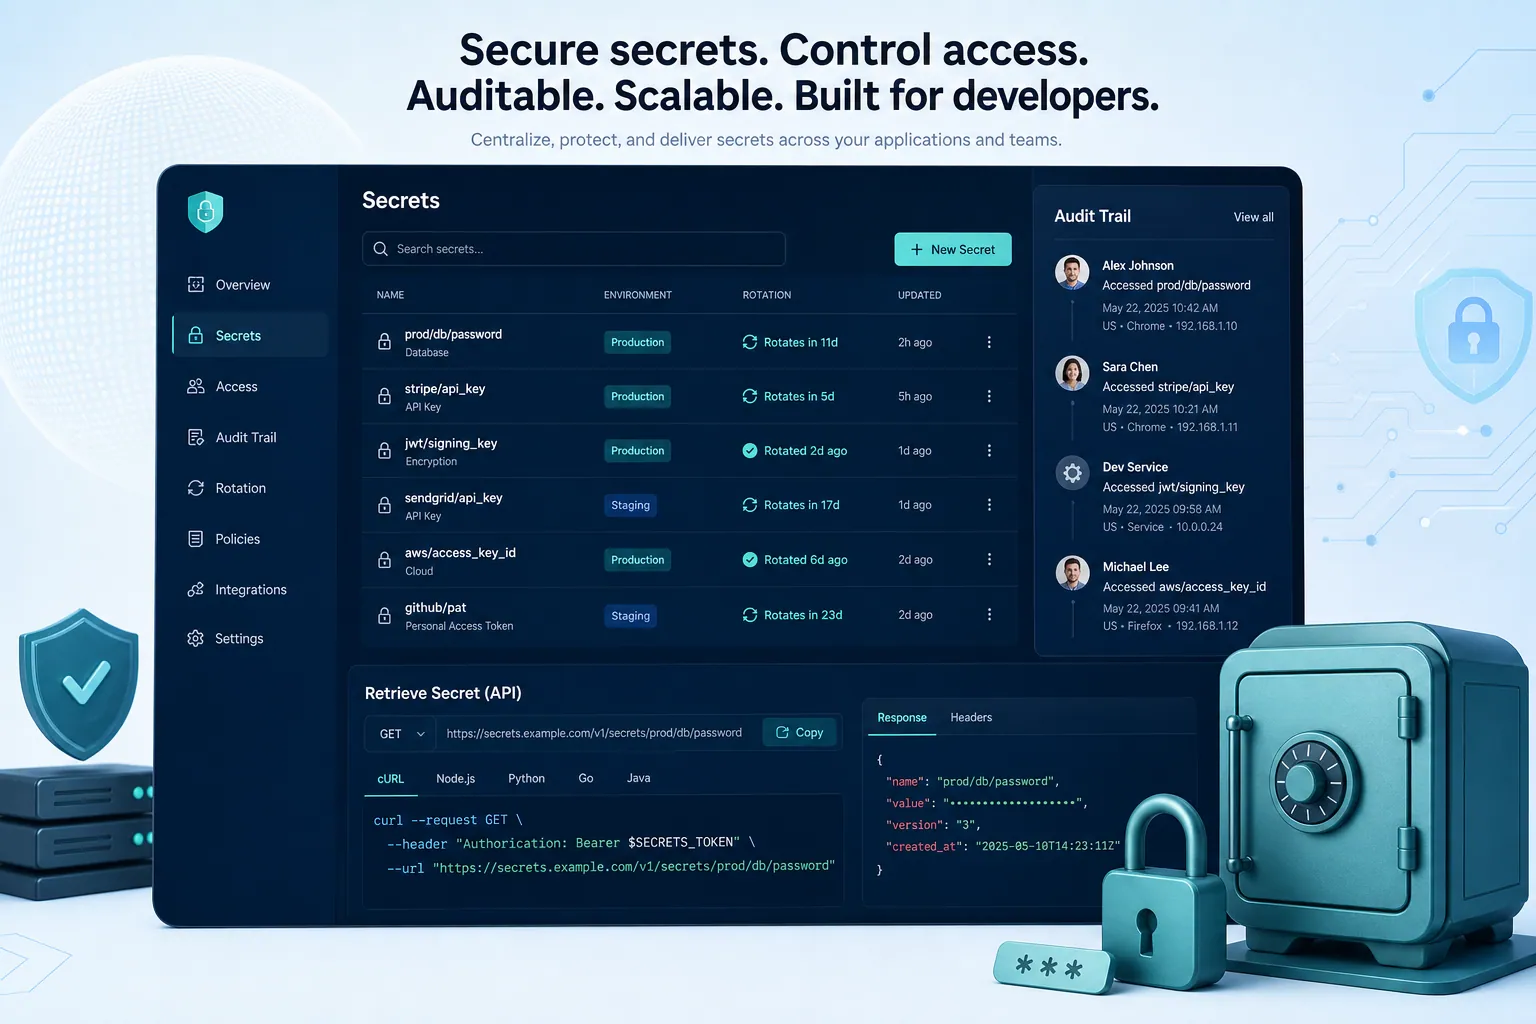
AES-256 with your database
Military-grade encryption with strong key derivation, backed by your own database - self-contained, not dependent on an external cloud vault.
Multi-tenant by design
One deployment serves every team or every customer without secrets crossing boundaries.
Full audit trail
Every read, write, and rotation logged - know exactly who touched what and when.
API-first automation
Built to be called from CI/CD pipelines, application code, or internal tooling directly.
Why it's different
Cloud-independent by design - run it entirely on your own infrastructure when data residency or sovereignty rules matter, without giving up the automation a modern vault should have.
Built for
Engineering and platform teams who need a real secrets manager, not another spreadsheet with a password on it.
- AES-256 with your database
- Multi-tenant by design
- Full audit trail
- API-first automation