
Financial Controls · Supported
SOX IT-GC
Sarbanes-Oxley Act - IT General Controls
SOX IT-GC
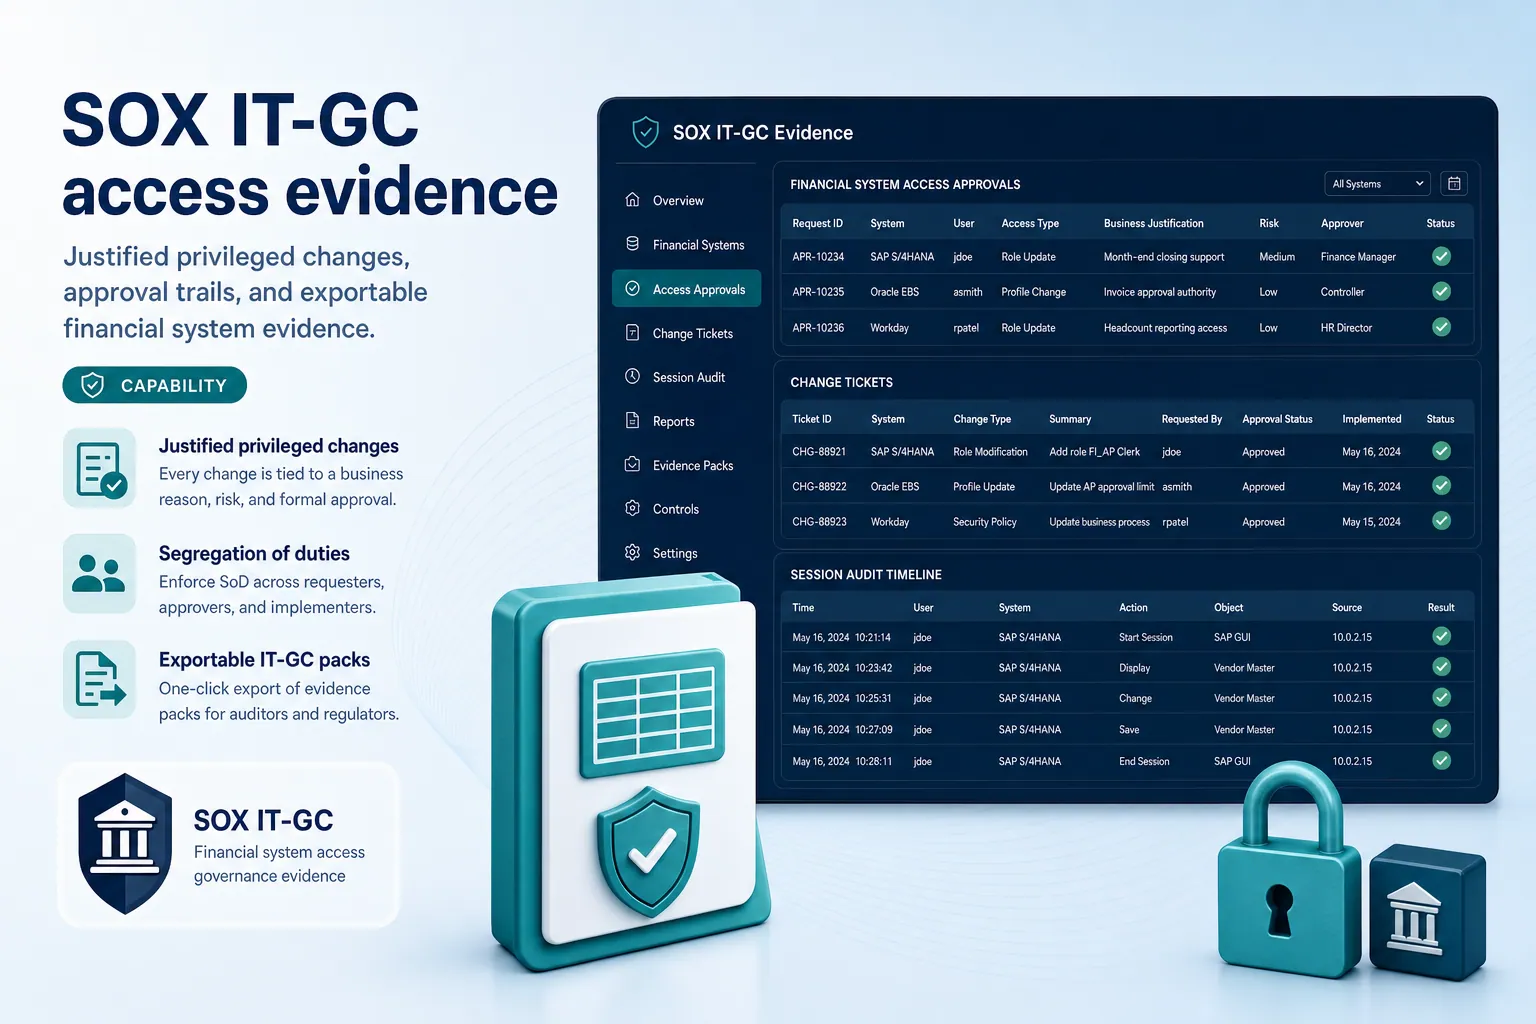
SOX IT general controls require justified privileged changes, approval trails, and evidence that financial systems stay under controlled access. ZenXPAM seeds SOX as a framework and maps request-approve-grant-connect-audit into clause-level controls and exportable packs for IT-GC reviews.
- Clause-level control mapping into IT-GC access and change narratives
- Just-in-time elevation instead of standing admin rights
- Hash-chained session and command-level evidence
- Signed evidence packs with an offline verifier for IT-GC reviews
What is SOX IT-GC?
The Sarbanes-Oxley Act (SOX) requires public companies to maintain effective internal controls over financial reporting. IT General Controls (IT-GC) are the foundational technology controls that support those financial controls - covering access management, change management, computer operations, and related privileged activity on systems that can affect financial data. Auditors look for evidence that privileged access is authorized, time-bounded, monitored, and reviewable. ZenXPAM supports SOX IT-GC programs by replacing standing privileges with just-in-time access, capturing approval trails, recording privileged sessions, and exporting structured evidence packs that map to access and change-control narratives.
Where is SOX IT-GC applicable?
SOX IT-GC expectations apply to U.S. public companies and many subsidiaries and service organizations that support financial reporting systems. They are especially relevant for ERP, financial close, revenue, payroll, and related infrastructure teams where privileged access can alter financial data or reporting integrity. Technology and managed service providers that operate in-scope systems for public companies are frequently asked to demonstrate equivalent privileged access controls. Any organization preparing for SOX audits, IPO readiness, or financial control attestations benefits from continuous privileged access evidence rather than quarterly evidence scrambles.
Features, benefits & risks
Key Features
- Clause-level control mapping into IT-GC access and change narratives
- Just-in-time elevation instead of standing admin rights
- Hash-chained session and command-level evidence
- Signed evidence packs with an offline verifier for IT-GC reviews
- Segregation of duties and dormant privileged user resolvers
Benefits
- Clear evidence for financial system privileged access
- Reduces standing privilege risk on SOX-in-scope systems
- Supports continuous control monitoring narratives
- Shortens audit evidence collection cycles
- Aligns operational PAM with IT-GC expectations
Risks
- Unaudited privileged changes on financial applications
- Standing admin rights that fail segregation-of-duties tests
- Missing approval and session evidence during SOX audits
- Control deficiencies that delay filings or remediation
- Increased external audit cost from manual evidence gathering