
Information Security · Supported
ISO 27001
ISO/IEC 27001:2022 Information Security Management
ISO 27001
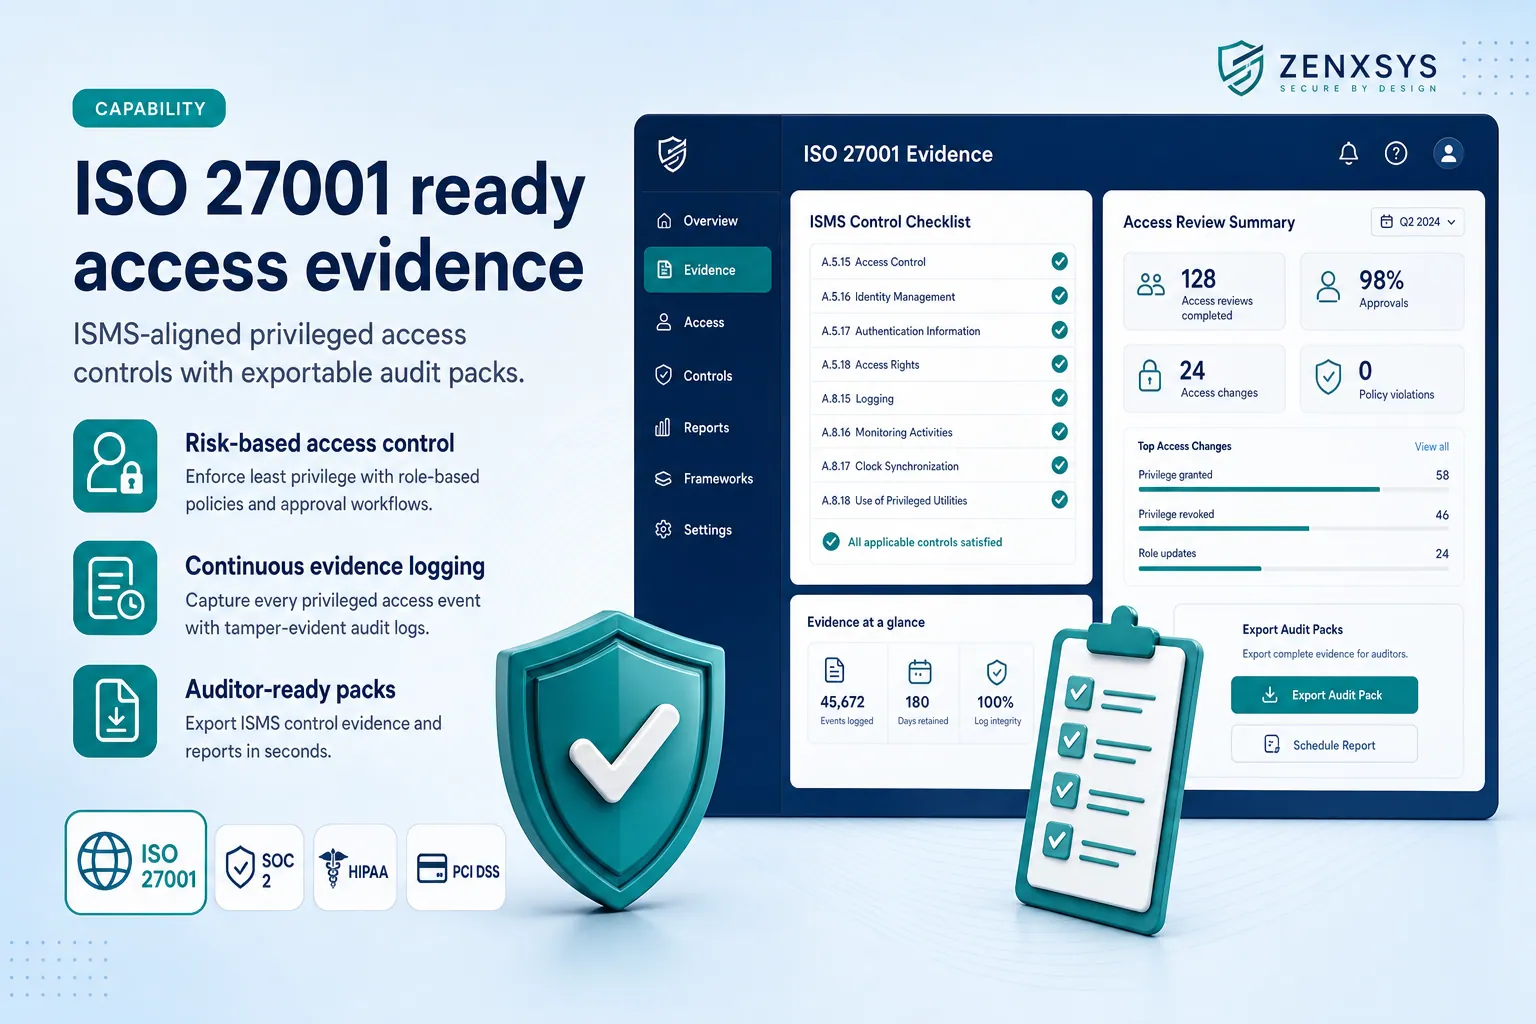
ISO/IEC 27001:2022 is the international standard for information security management systems. ZenXPAM seeds it as a framework, maps internal privileged access controls to named Annex A clauses, scores them continuously, and exports signed evidence for your ISMS audit. ZenXPAM is not itself ISO 27001 certified.
- Annex A clause-level mapping from ZenXPAM internal controls
- Continuous automated control checks with an ISO 27001 score and drill-down
- Access certification campaigns for privileged accounts and roles
- Hash-chained audit trail behind every control assertion
What is ISO 27001?
ISO 27001 is an international standard that specifies requirements for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). It provides a systematic approach to managing sensitive company information, ensuring it remains secure. The standard helps organizations manage the security of assets such as financial information, intellectual property, employee details, or information entrusted by third parties. ISO 27001 is based on a risk management approach, requiring organizations to identify information security risks and implement appropriate controls to mitigate or eliminate them.
Where is ISO 27001 applicable?
ISO 27001 is applicable to organizations of all sizes and types, across all industries. It is particularly relevant for organizations that handle sensitive information, including financial institutions, healthcare providers, technology companies, government agencies, and any business that processes, stores, or transmits confidential data. The standard is globally recognized and can be implemented by any organization seeking to demonstrate their commitment to information security. It is especially valuable for organizations that need to comply with regulatory requirements, want to improve their security posture, or need to assure customers and stakeholders about their information security practices.
Features, benefits & risks
Key Features
- Annex A clause-level mapping from ZenXPAM internal controls
- Continuous automated control checks with an ISO 27001 score and drill-down
- Access certification campaigns for privileged accounts and roles
- Hash-chained audit trail behind every control assertion
- Signed evidence packs with an offline verifier for your ISMS auditor
Benefits
- Supports the access control clauses your ISMS is assessed on
- Replaces screenshot evidence with continuous, dated control checks
- Shortens ISMS internal audit and surveillance preparation
- Gives auditors evidence they can verify without platform access
- Keeps privileged access aligned to the risk treatment plan
Risks
- Data breaches leading to unauthorized access to sensitive information
- Non-compliance with regulatory requirements resulting in legal penalties
- Loss of customer trust and reputation damage
- Financial losses from security incidents and recovery costs
- Operational disruptions from security breaches