Non-Human Identity Governance
Your service accounts have more access than most of your employees. Time someone managed that.
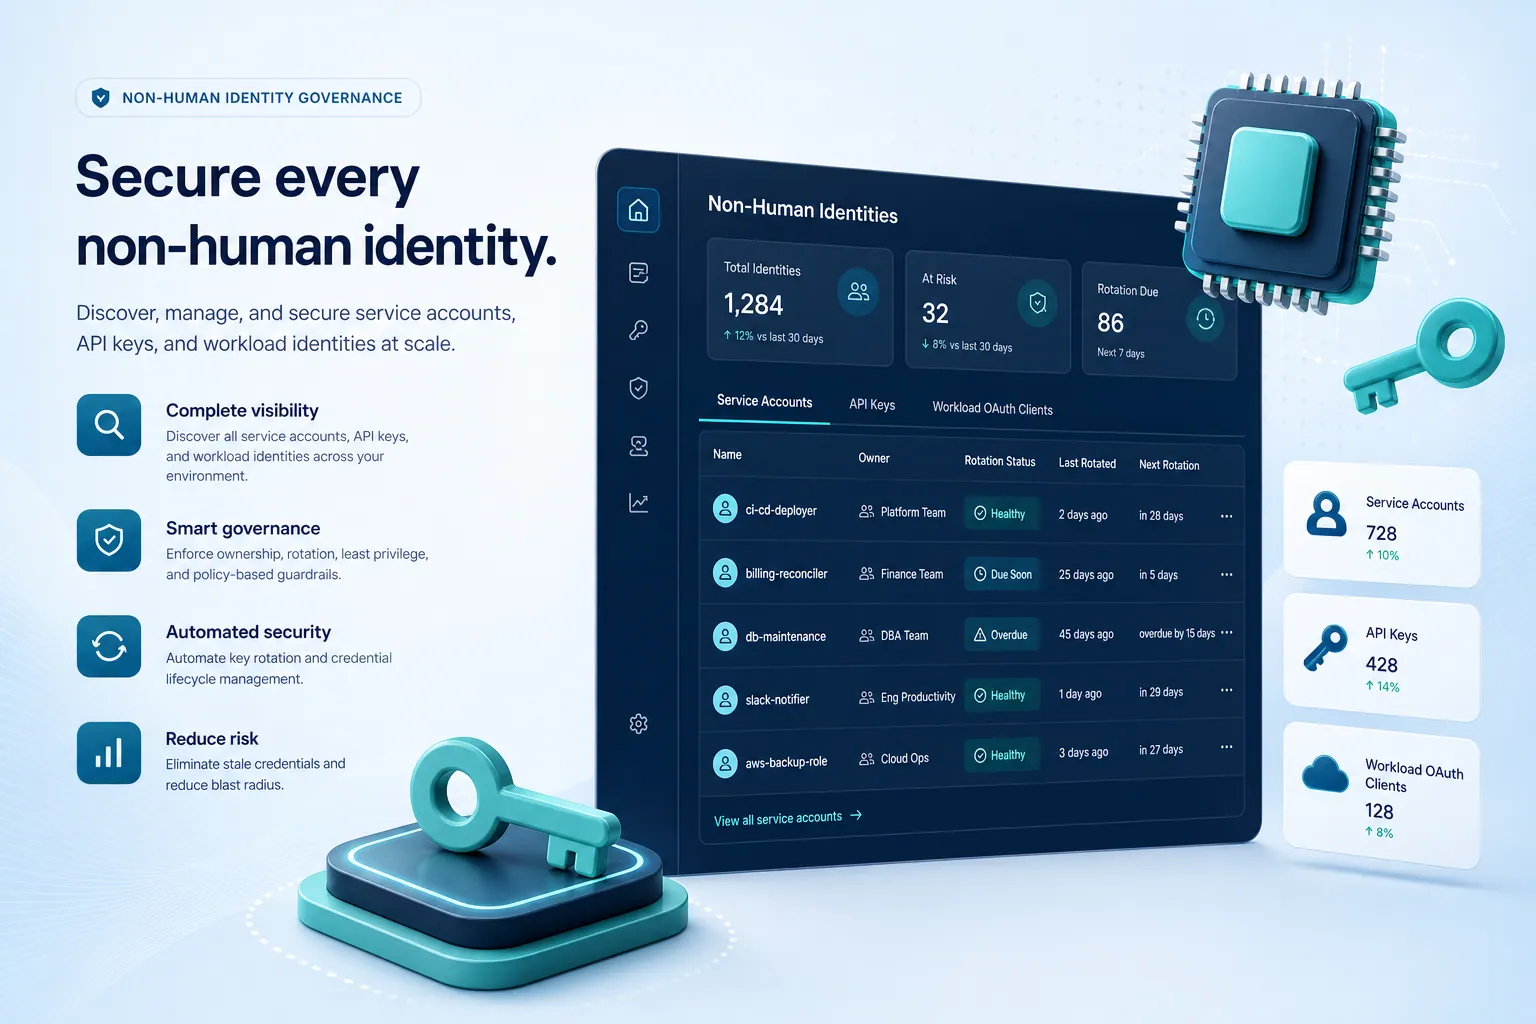
Machine identities - service accounts, API keys, workload credentials - now outnumber human users in most enterprises, and almost nobody governs them the way they govern people. NHI Governance brings the same lifecycle discipline to machine identity that you already apply to human access: known ownership, credential rotation, and visibility into what every non-human identity can actually touch.
M2M
Identity visibility
OAuth
Workload creds
Lifecycle
Own · rotate · revoke
Same
Platform as humans
How it works
AWS, Azure & GitHub connectors
Dedicated connectors for AWS IAM, Azure Service Principals, and GitHub PATs - with circuit-breaker, retry, dead-letter, and egress-policy resilience behind delivery.
Centralized machine-identity visibility
See every machine identity and what it’s authorized to access - ownership included, not orphaned keys.
Lifecycle governance
Ownership, rotation, and deprovisioning for accounts that traditionally get created once and forgotten.
Same identity platform
Built on the same platform securing your human users - not a bolted-on side system.
Why it's different
This is one of the fastest-growing gaps in enterprise security, and most organizations still have zero answer for "who owns this API key and does it still need this access." ZenXPAM answers it with real connectors to the three platforms every buyer already runs.
Built for
Platform and security teams whose machine-to-machine access has quietly outgrown every spreadsheet trying to track it.
- AWS, Azure & GitHub connectors
- Centralized machine-identity visibility
- Lifecycle governance
- Same identity platform