Vendor PAM
Give vendors access. Never give them the password.
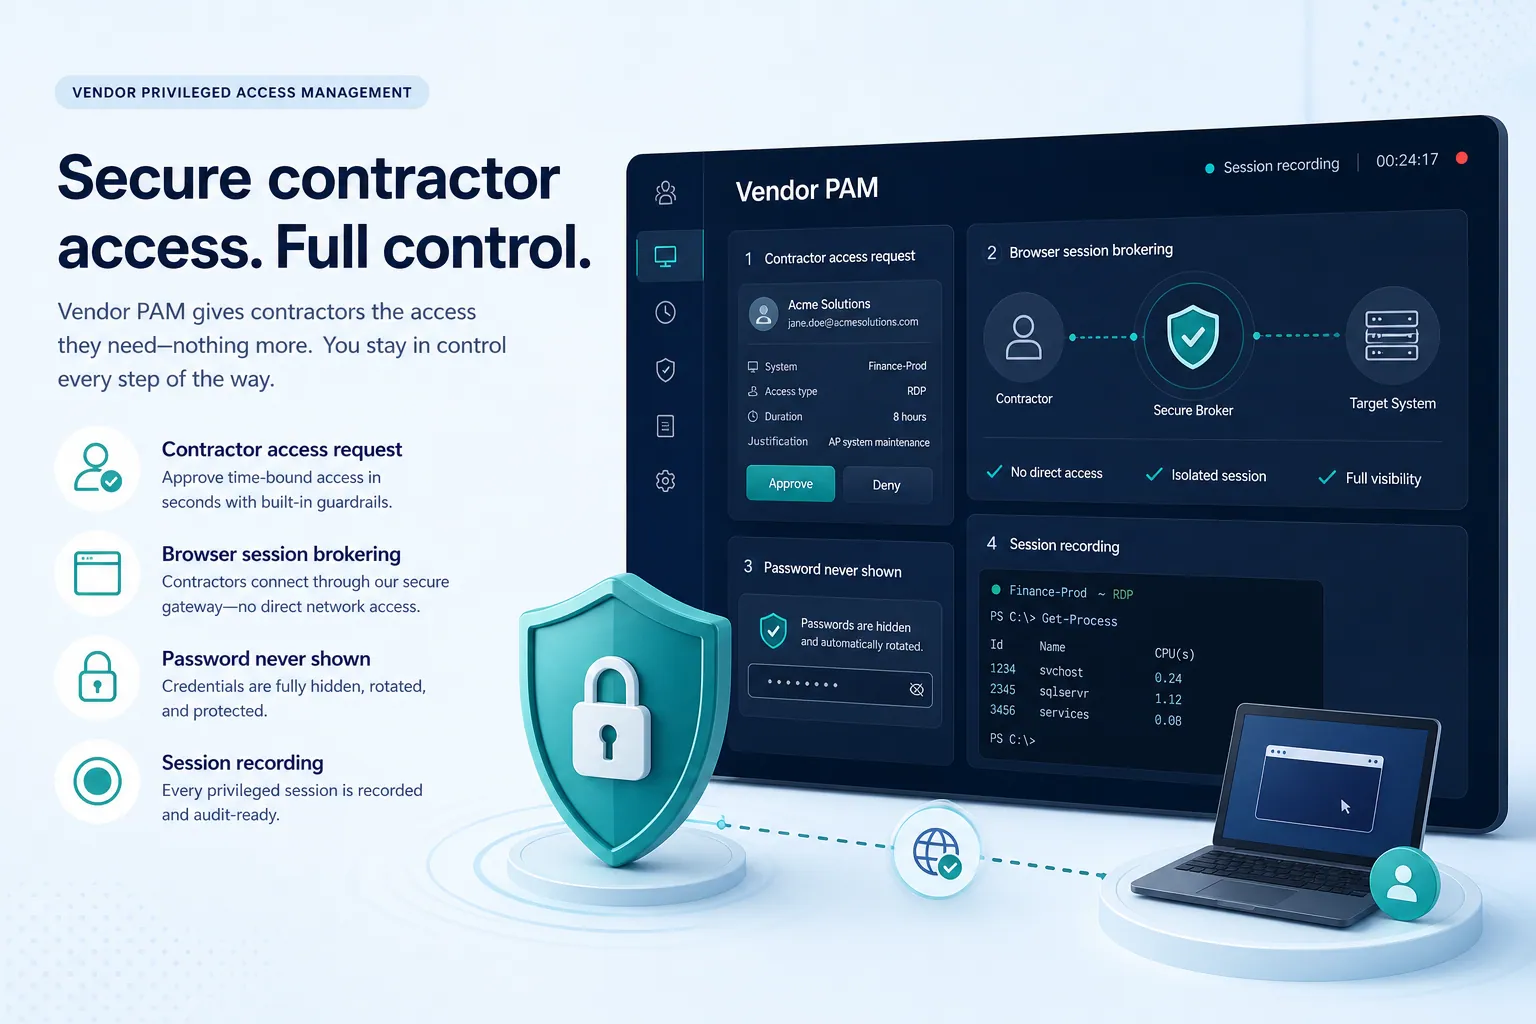
Third-party access is where PAM programs quietly fail - vendors get VPN credentials, shared logins, standing accounts nobody remembers to revoke. Vendor PAM flips that: contractors and remote admins connect through the browser, the platform injects credentials server-side, and every session is recorded start to finish. The vendor never sees a password. You never lose visibility.
0
Passwords to vendors
Browser
Clientless access
Full
Session recording
Isolated
Jump-server routing
How it works
Clientless RDP, SSH & web
No VPN, no agent, no software for the vendor to install - access through the browser.
Server-side credential injection
Passwords injected at connection time; never displayed, copied, or exposed to the end user.
Searchable session playback
Full session recording so "what did the vendor actually do" has a real answer.
Jump-server isolation
Jump-server based routing keeps vendor traffic isolated from the rest of your network.
Why it's different
Built for the access relationship you don’t fully trust - not retrofitted from an internal-admin tool. Onboard a vendor in minutes, offboard them the same way, and never hand over a credential either way.
Built for
Organizations managing contractors, MSPs, and remote vendors who need access to production systems without becoming a standing liability.
- Clientless RDP, SSH & web
- Server-side credential injection
- Searchable session playback
- Jump-server isolation