Privileged Account Hygiene Scanner
Find the admin accounts nobody remembers creating.
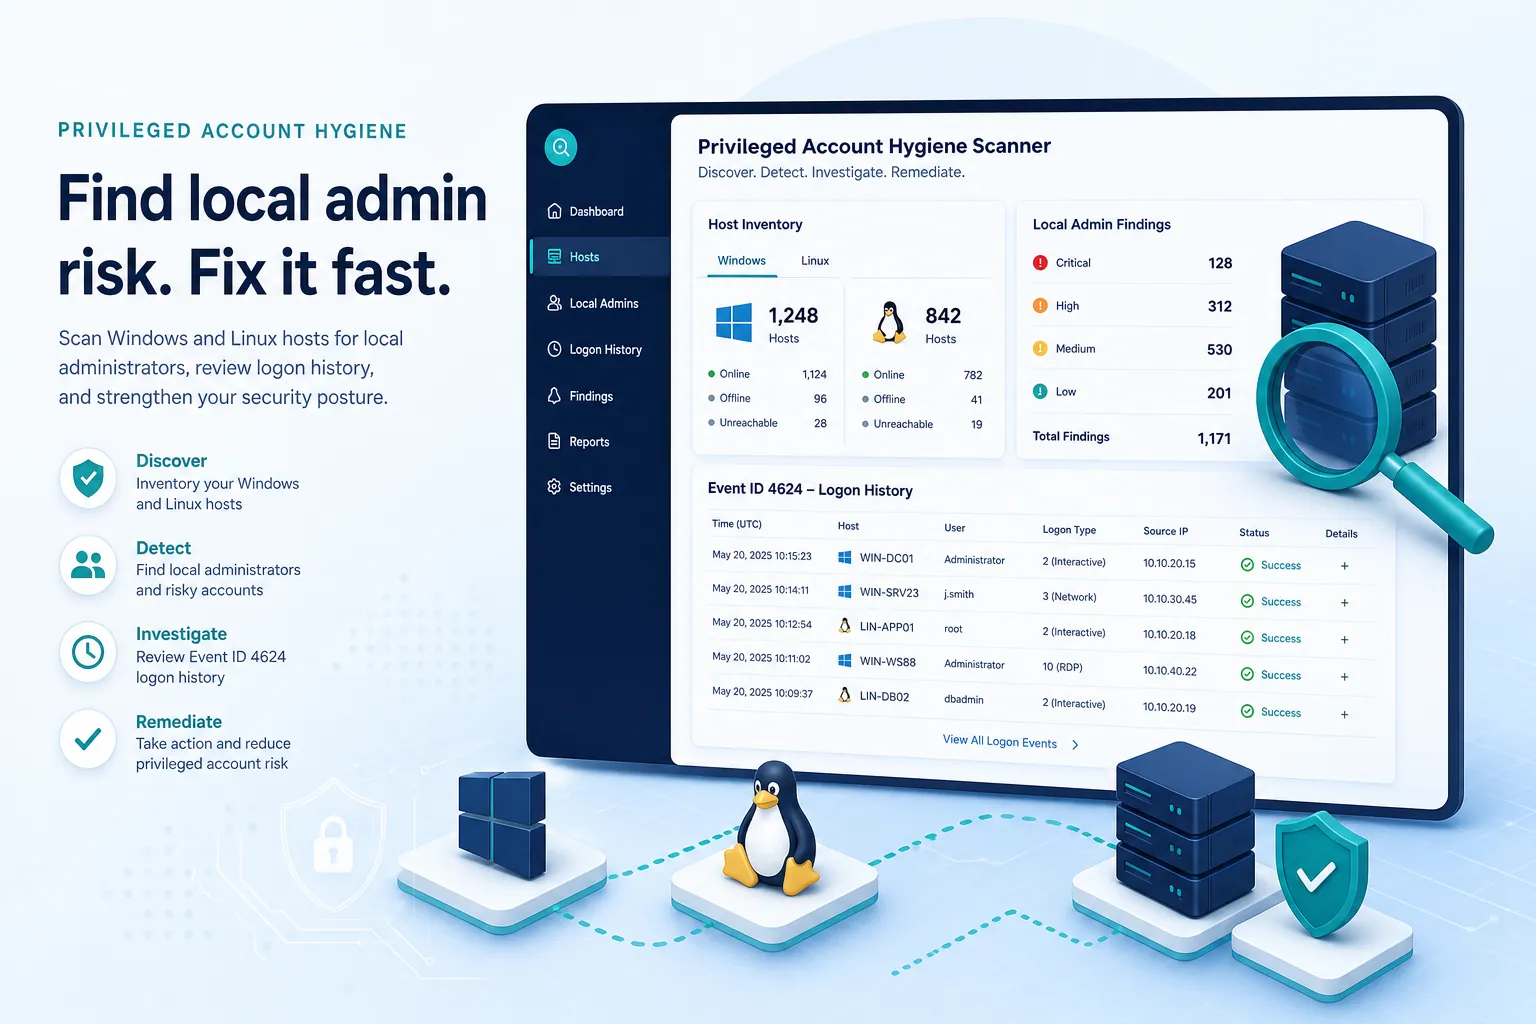
Every environment accumulates privilege it didn’t mean to keep - a local admin account from a project that ended two years ago, a service account with a password that’s never rotated, an install nobody approved. The Hygiene Scanner sweeps your estate over SSH and WinRM and surfaces exactly where standing privilege is hiding, without pretending to be a full endpoint management suite.
SSH
& WinRM sweep
Win
+ Linux inventory
4624
Logon history
Focus
Privilege risk only
How it works
Host inventory
Windows and Linux: local users, groups, running services, installed applications, last logon activity.
Windows logon history
Event ID 4624 pulled from the Security log - see who actually accessed what, from where.
Works with partial credentials
Works with or without stored credentials; partial results are still useful, not a hard failure.
Narrow by design
Finds privileged-account risk - it doesn’t try to patch, monitor, or replace your existing endpoint tools.
Why it's different
This isn’t trying to out-build Tanium or Qualys. It’s a focused answer to one question: where is unmanaged privilege sitting in my environment right now?
Built for
Security teams doing access reviews who are tired of manually cross-referencing account lists across every system by hand.
- Host inventory
- Windows logon history
- Works with partial credentials
- Narrow by design