
Security & Compliance
Security & Compliance
Enterprise-grade security standards and compliance certifications to protect your business
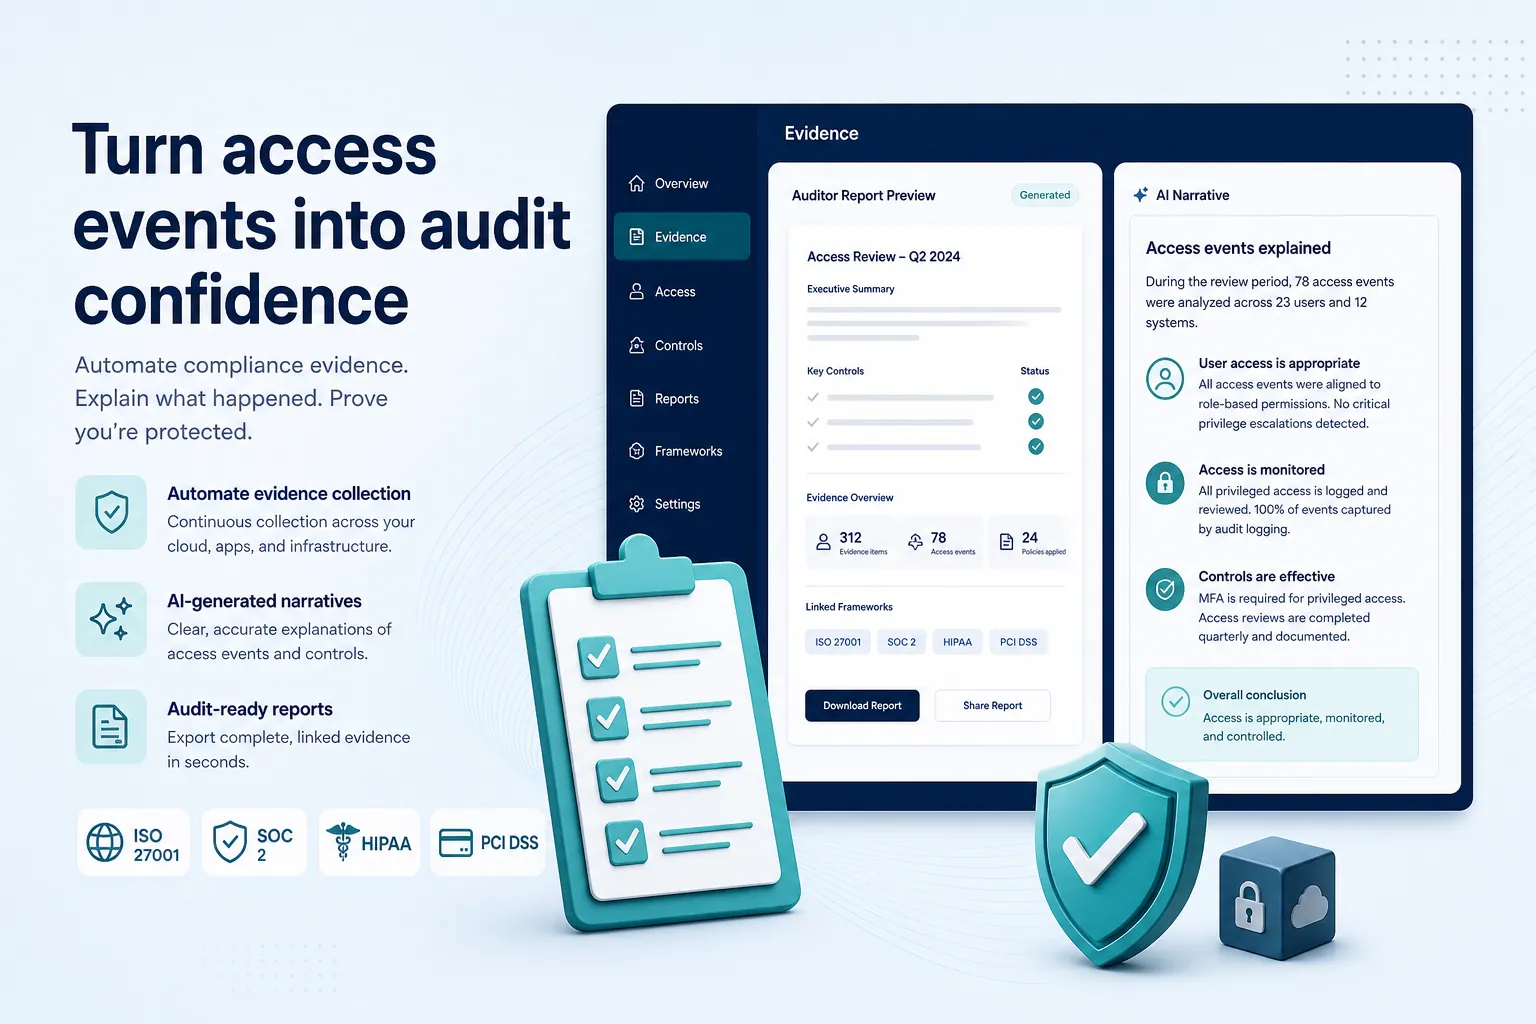
Supported, Mapped, Evidence-Aligned
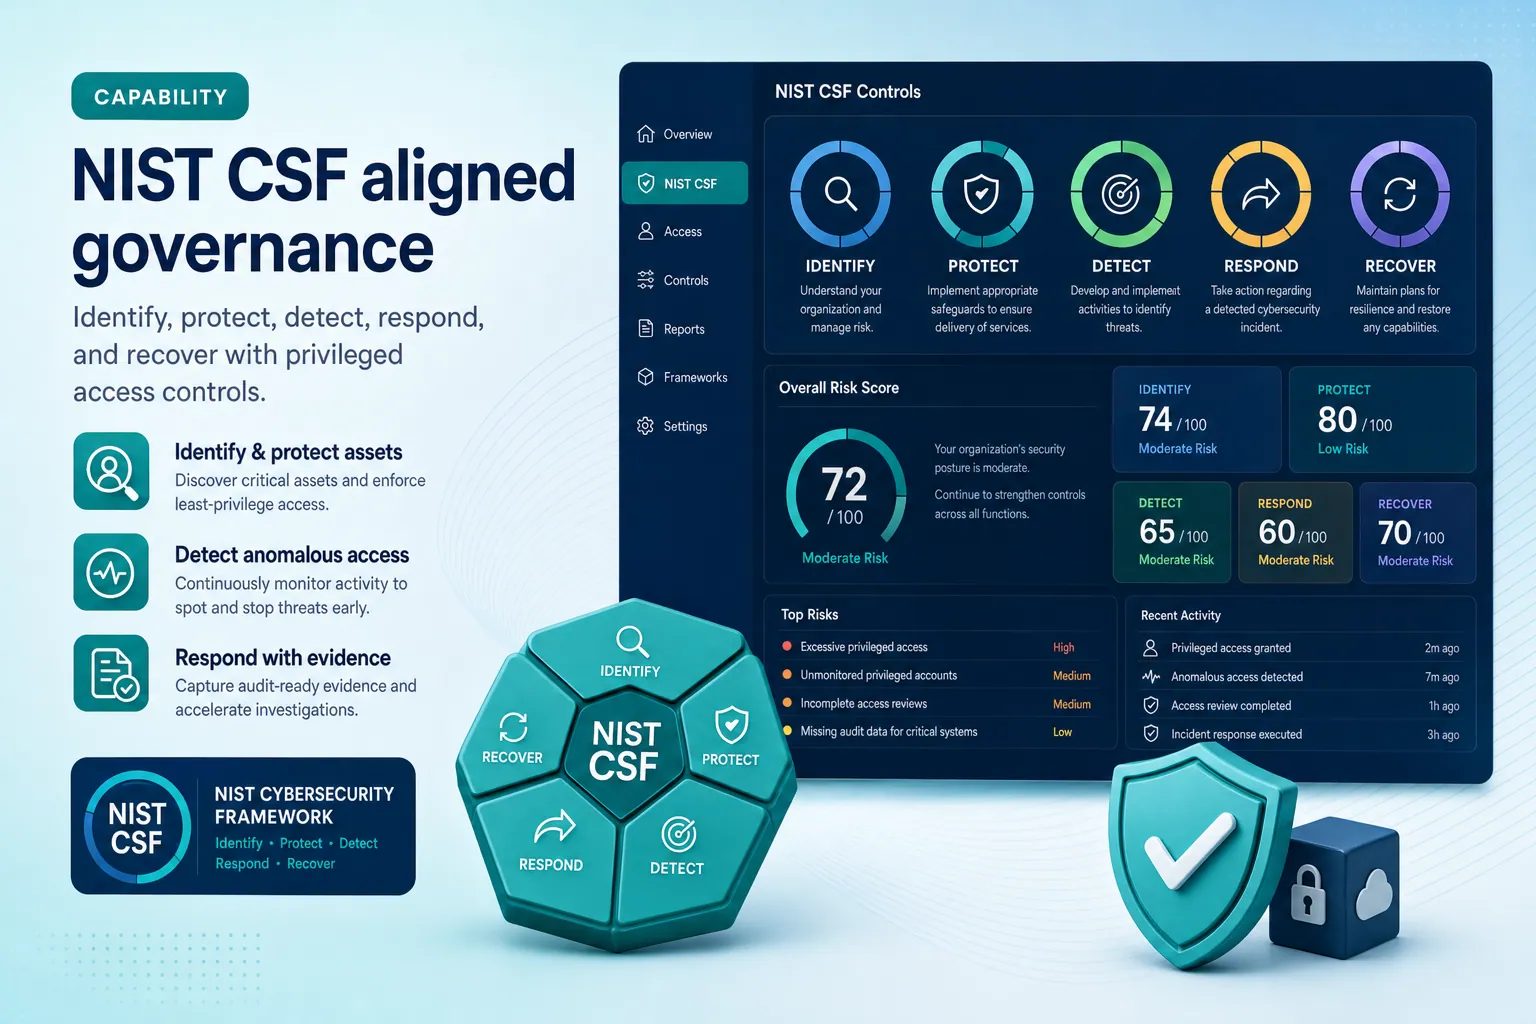
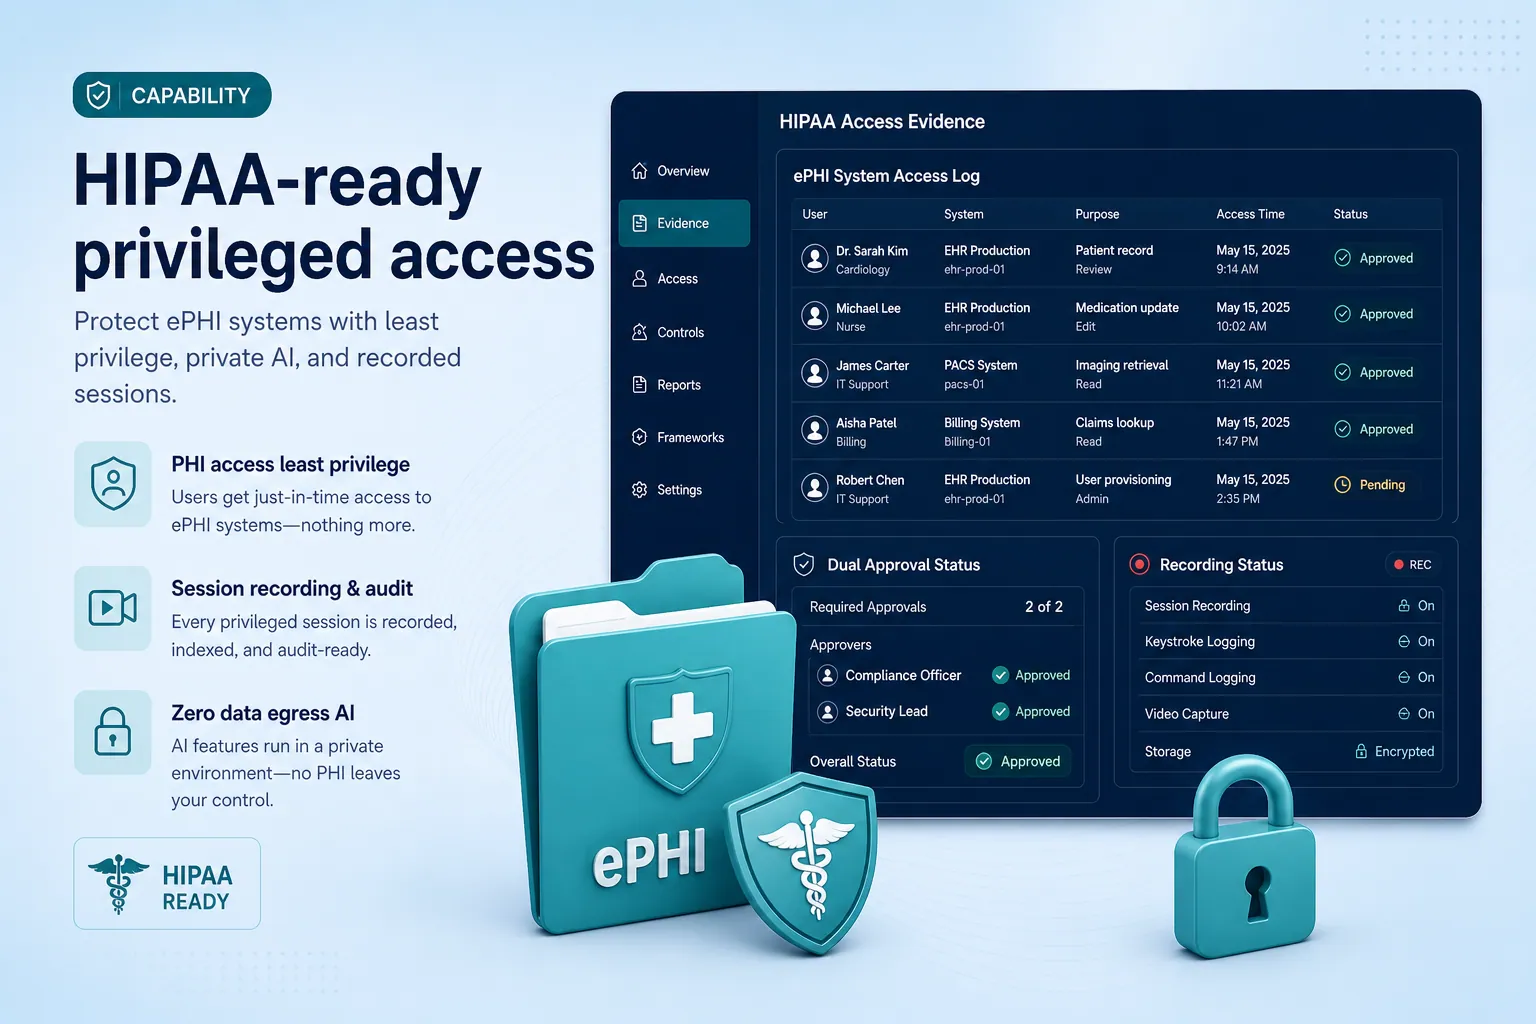
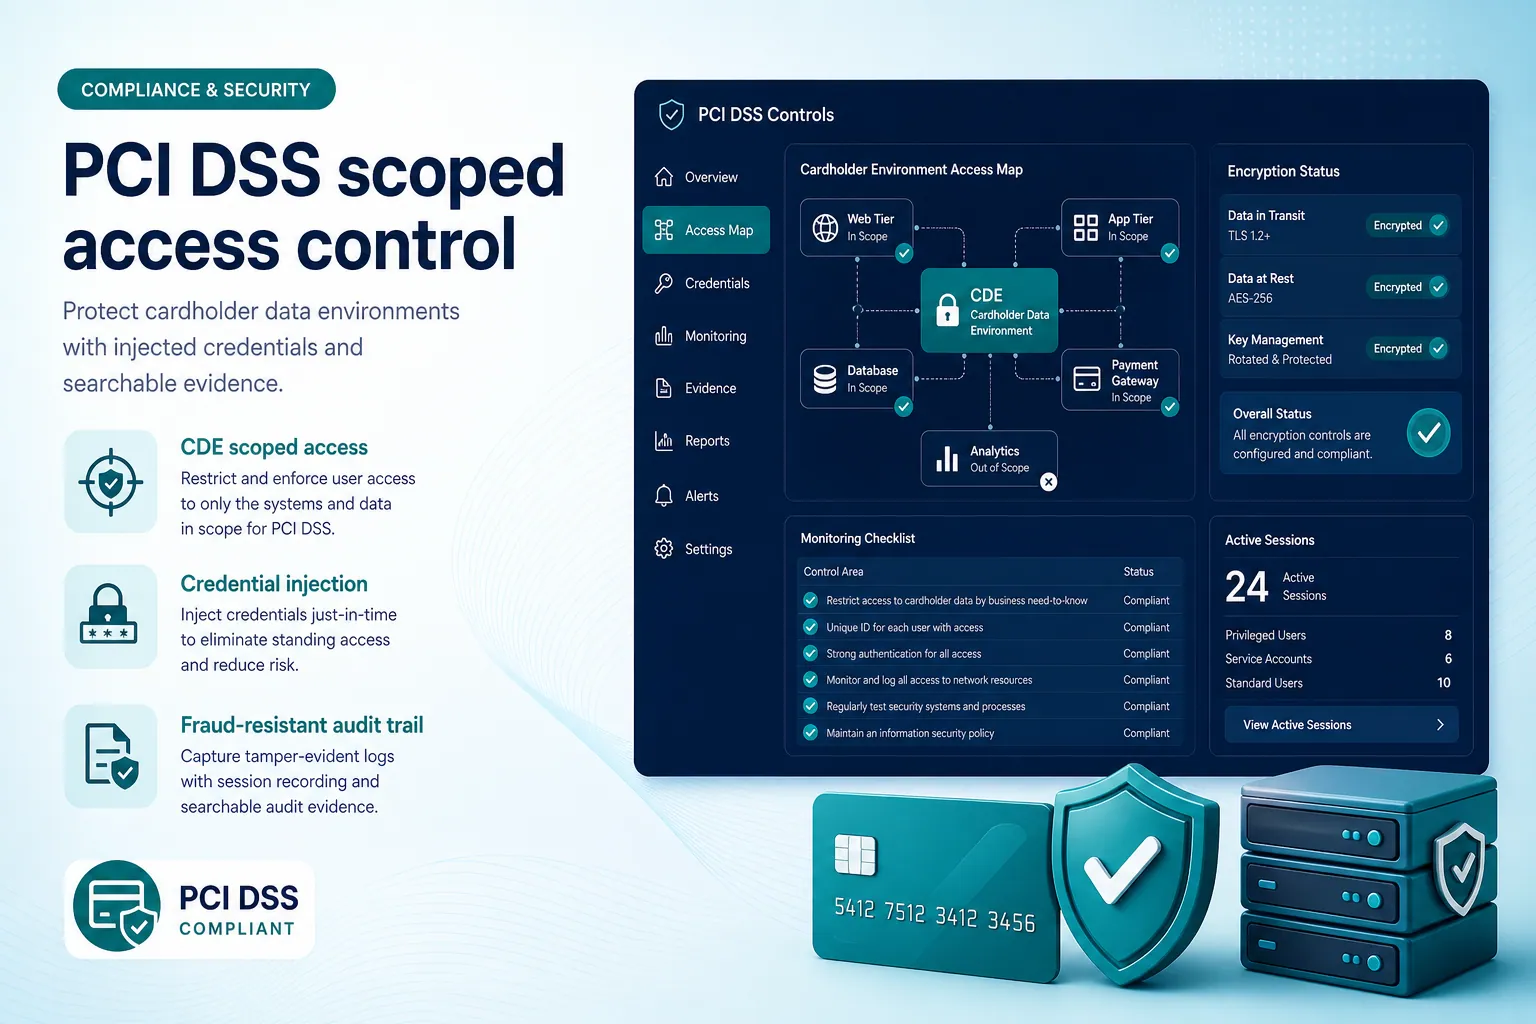
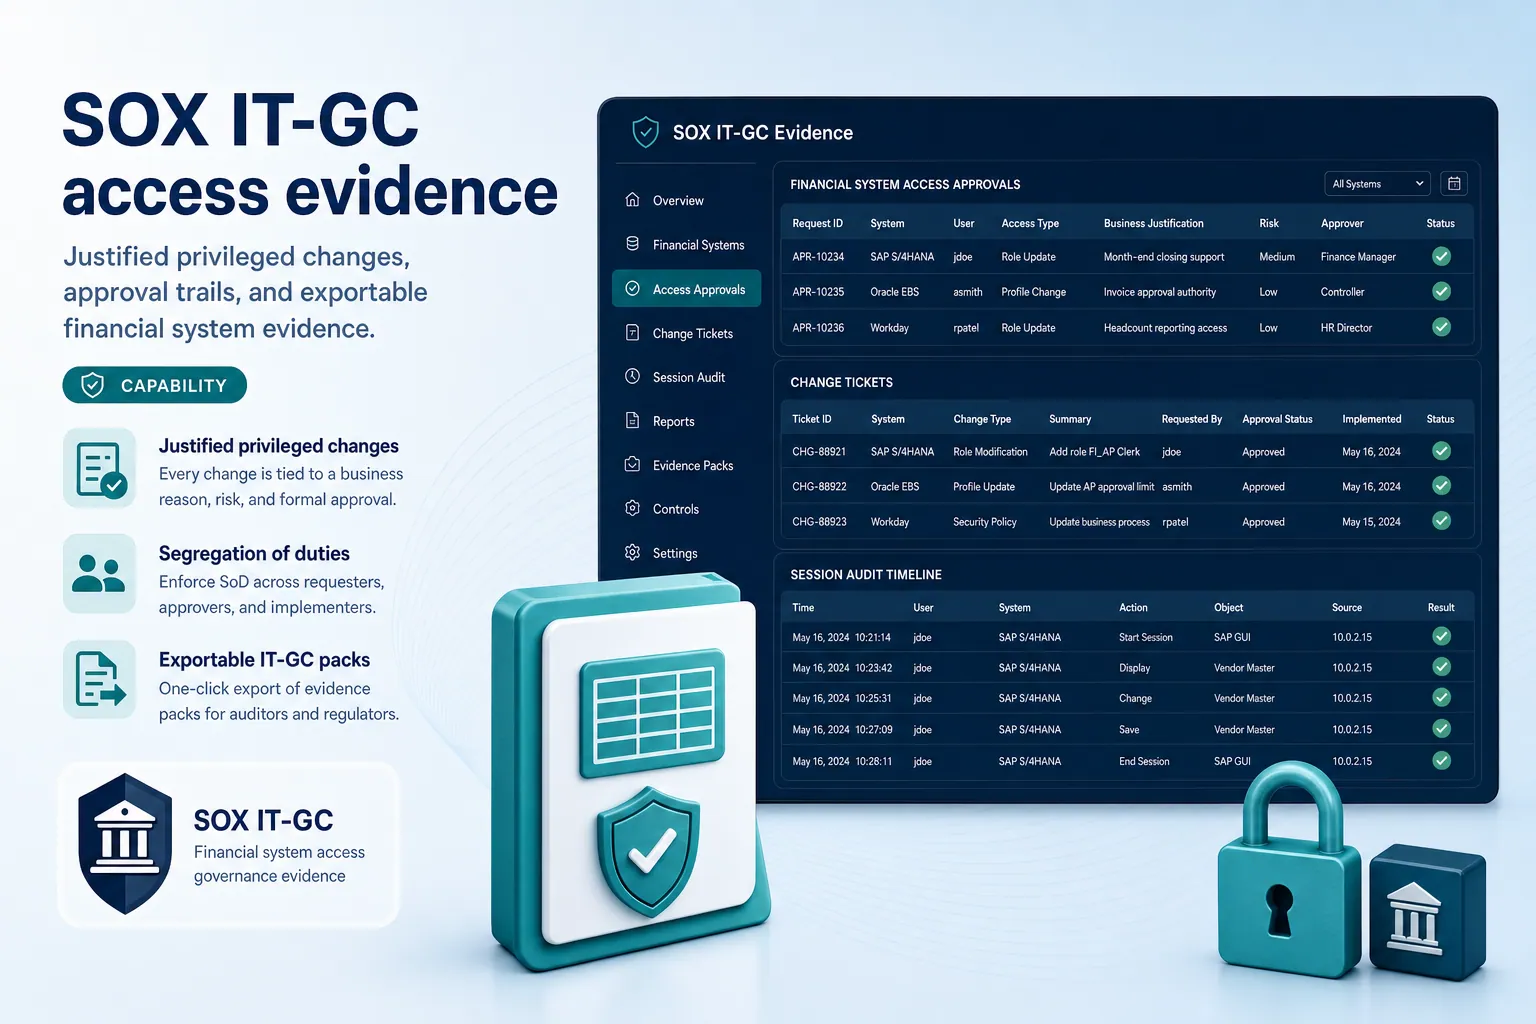
ZenXPAM seeds eight external frameworks plus its own internal control library. One internal control maps to named clauses in several frameworks at once, continuous automated checks produce a per-framework score with drill-down, access certification campaigns run periodic reviews, every audit record sits in a hash-chained trail, and evidence packs export with per-file hashes under a signed manifest that an offline verifier can check without trusting the platform. None of this is a certification claim - it is the evidence your own auditors and assessors work from.
Security and Compliance Practices
How ZenXPAM produces framework evidence, and how Zenxsys runs its own security
Clause-Level Control Mapping
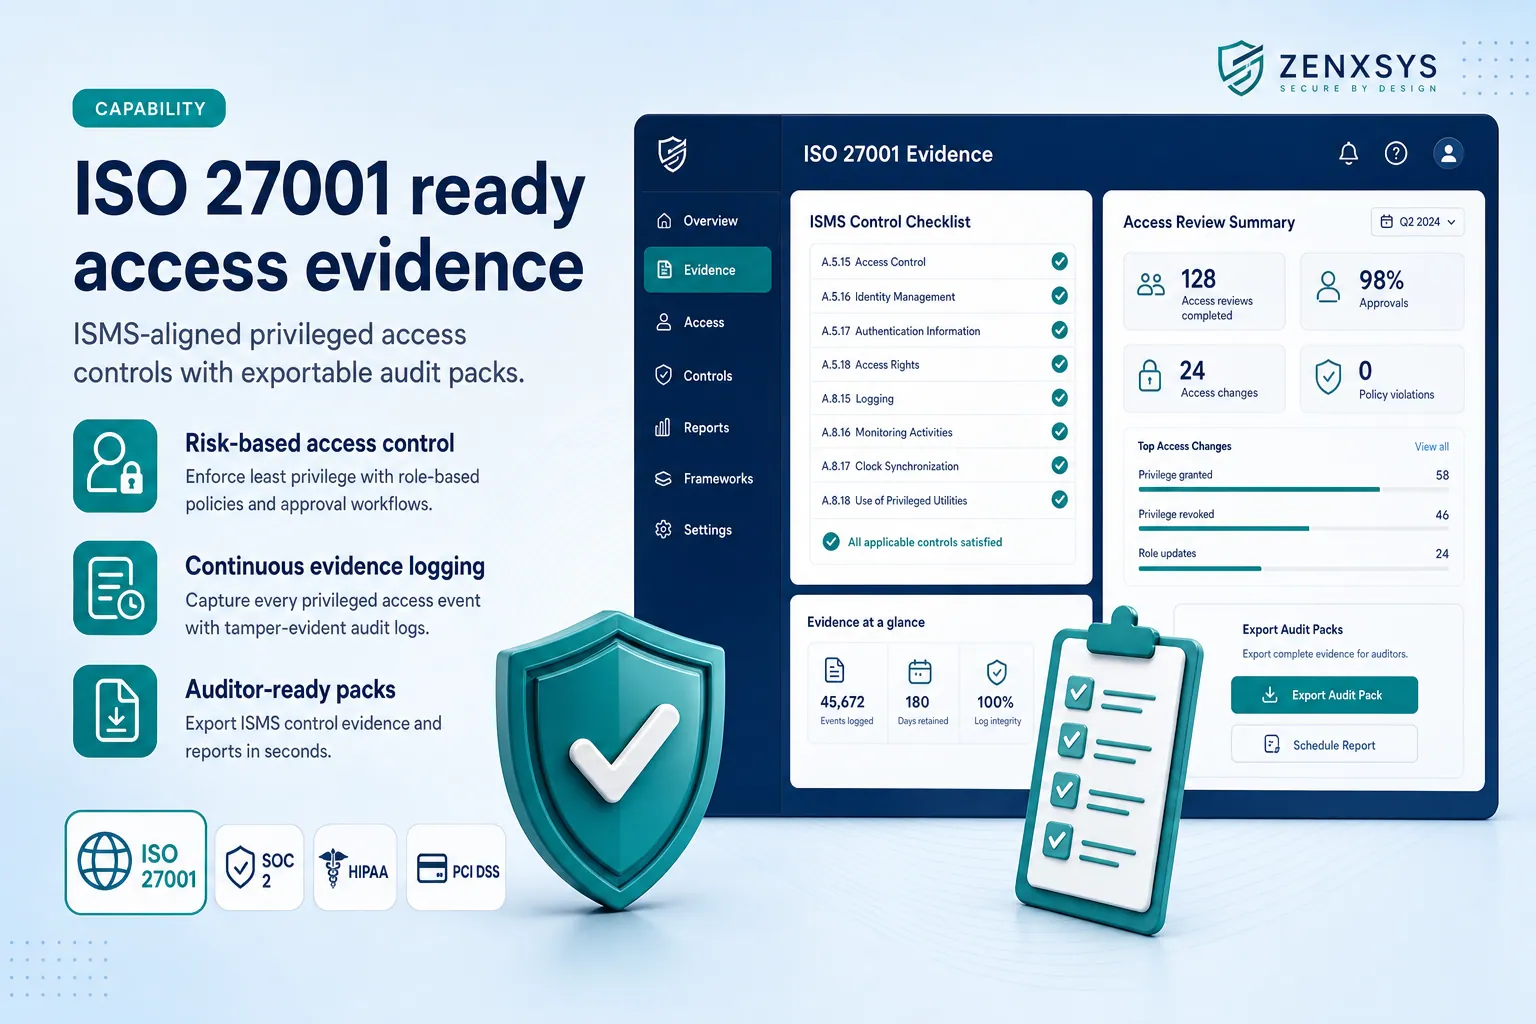
One internal ZenXPAM control maps to named clauses in several frameworks at once - a single access control can answer SOC 2, ISO 27001, PCI DSS, HIPAA and NIST CSF together, so evidence is gathered once and reused.
Continuous Control Checks
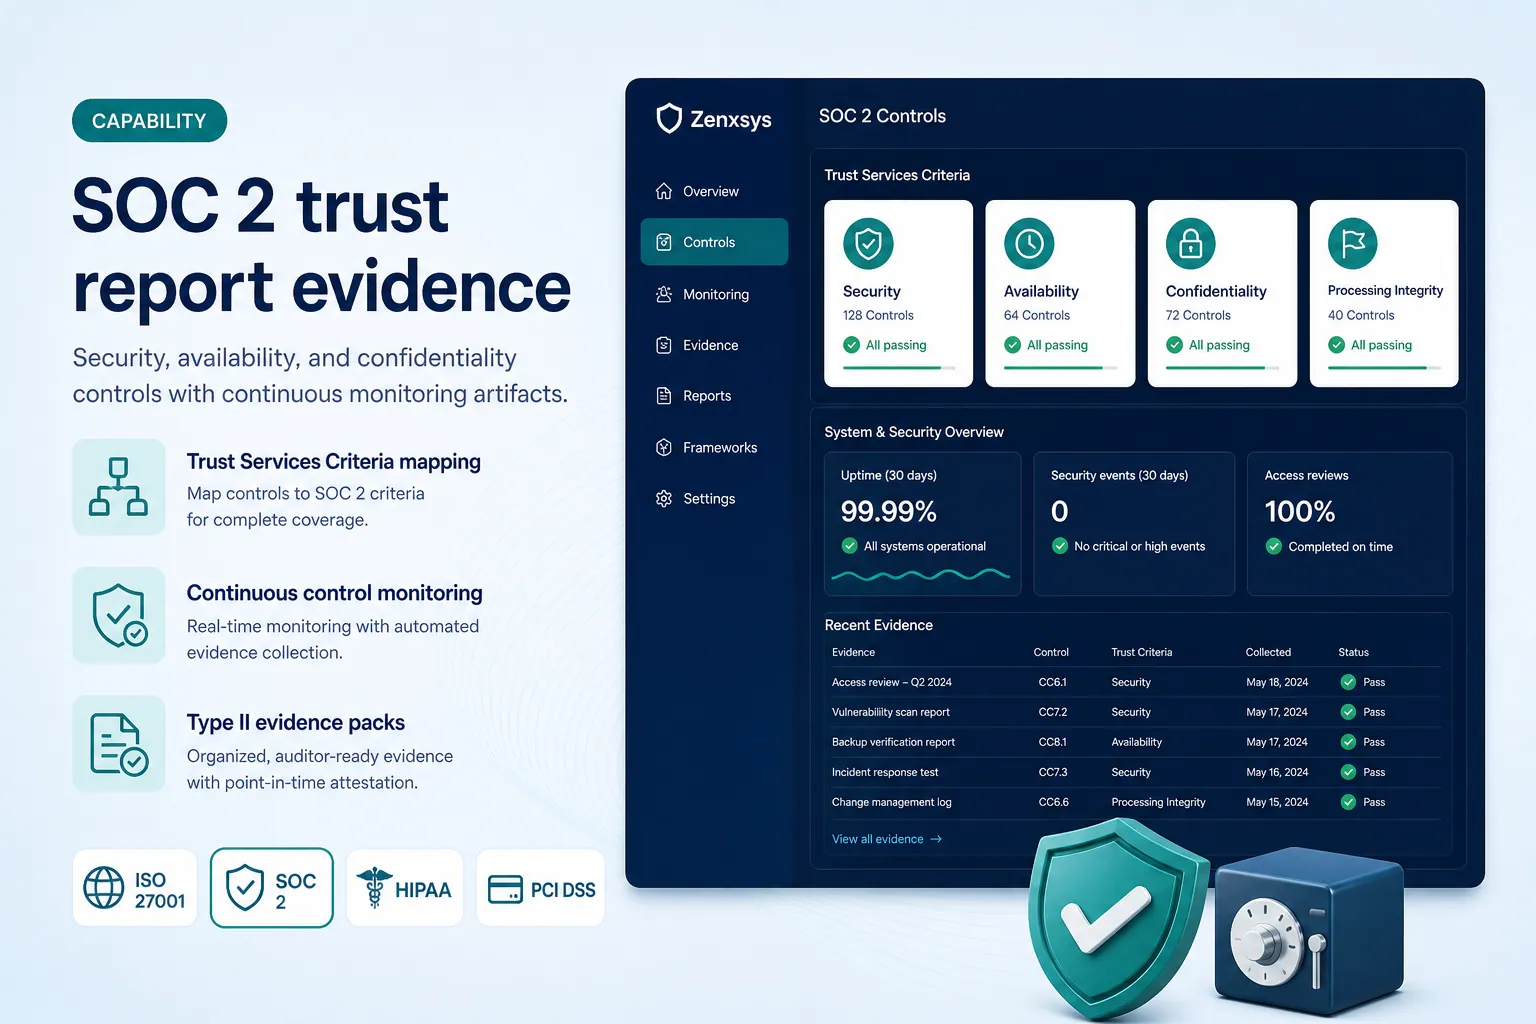
Automated checks run against the seeded frameworks and produce a per-framework score with drill-down, alongside control exceptions, policy drift detection, and segregation-of-duties and dormant-account resolvers.
Access Certification Campaigns
Periodic reviews of privileged accounts, roles and entitlements run quarterly, semi-annually or annually, with automatic escalation of overdue reviews and a recorded decision for every line.
Hash-Chained Audit
Every privileged request, approval, session and command lands in a hash-chained audit trail with a uniform event envelope, forwardable to SIEM as syslog over TLS or as JSON, CEF or LEEF over a signed webhook.
Signed Evidence Packs
Audit-readiness packs export on demand with per-file SHA-256 hashes under a signed manifest, plus an offline verifier so an auditor can check the evidence without access to, or trust in, the platform.
Encryption and Key Handling
Traffic is protected with TLS. Vault secrets are encrypted with AES-256-CBC and HMAC-SHA256 under a PBKDF2-SHA256 derived key; backup bundles and platform field encryption use AES-256-GCM; grants and evidence are signed with ES256. The master key is environment-managed - there is no KMS or HSM integration today, and the cryptography is standards-based but not formally validated.
Incident Response
A documented incident response process covers detection, containment and recovery. In ZenXPAM, emergency break-glass access stays available and fully audited even where an entitlement has lapsed, so a licence window never blocks an incident response.
Business Continuity
Backup and disaster recovery procedures cover the platform and the vault, with a documented credential disaster-recovery architecture and runbook so privileged access can be restored, not just the database.
Security Training
Regular security awareness training for all employees ensures everyone understands and follows security best practices and policies.
Why Compliance Matters
Our commitment to security and compliance provides tangible benefits for your business
Risk Mitigation
Reduce security risks and protect against data breaches with industry-leading security controls.
Regulatory Compliance
Meet the access control requirements in eight seeded frameworks from one set of internal controls, mapped clause by clause.
Customer Trust
Build customer confidence with transparent security practices and evidence that stands up to independent verification.
Faster Assurance
Answer security questionnaires and audit requests with evidence rather than assurances, and keep deals moving.
Ready to Secure Your Business?
Let's discuss how our security and compliance framework can protect your organization.
Get Security Consultation