
Applied AI
Making AI Safe for Sensitive Workflows
"Private AI" gets used loosely. Here's what it actually means, and how to get value without exposing regulated data.
Zenxsys Team · August 14, 2026 · 5 min read
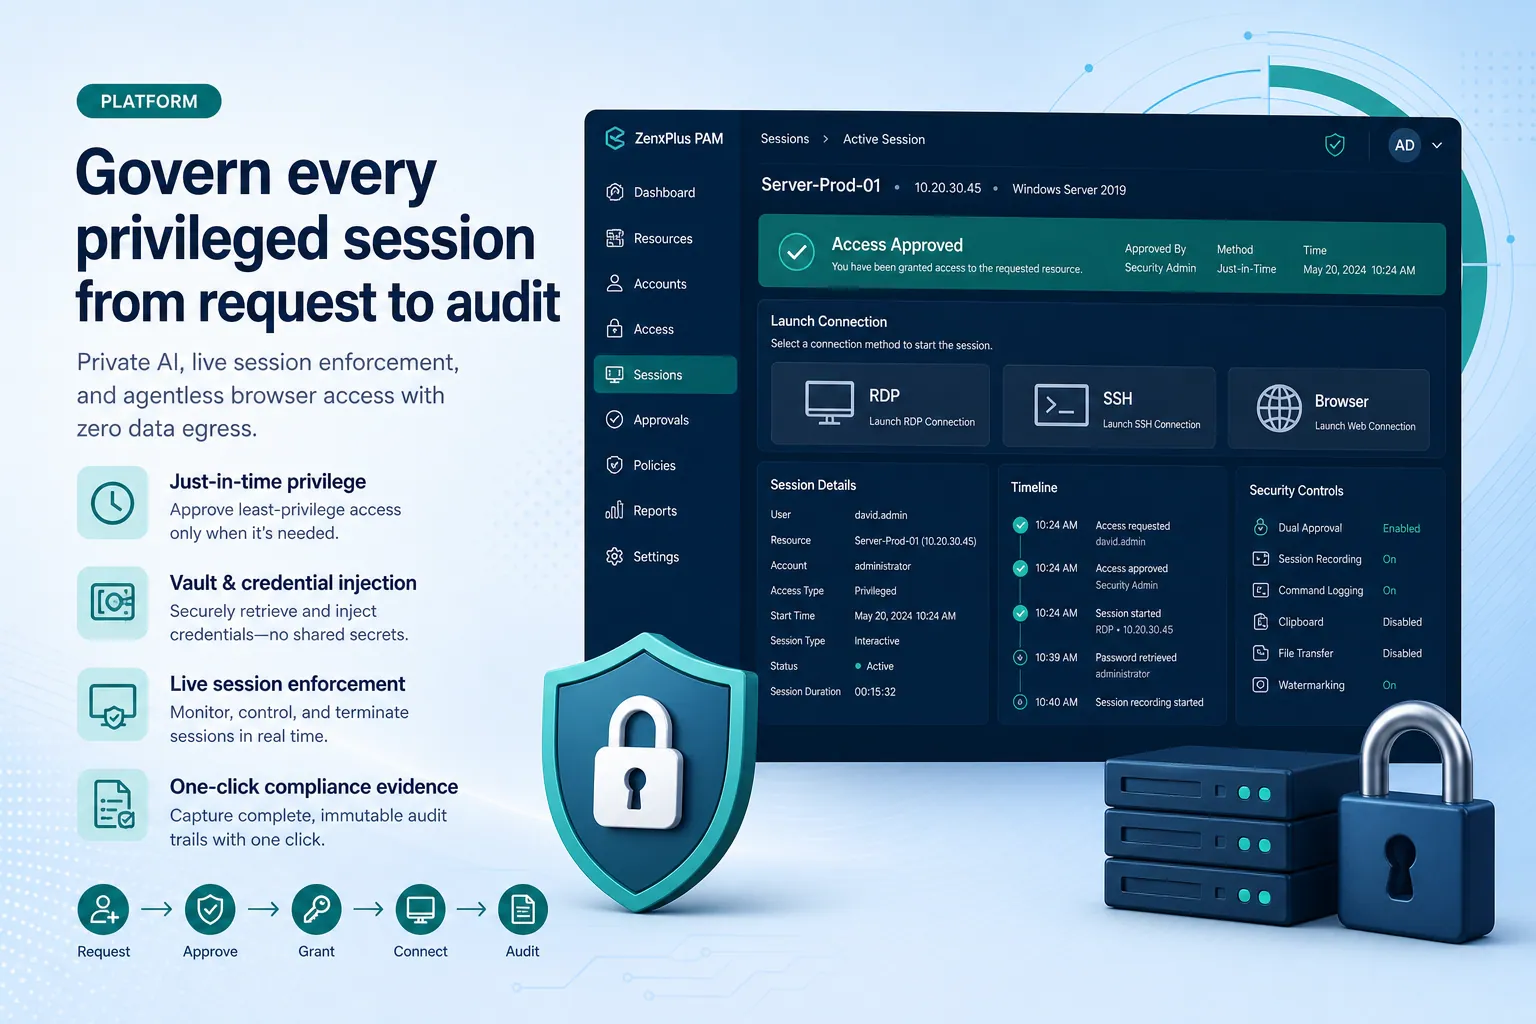
Teams want to point AI at their most valuable data - runbooks, incident history, privileged session logs - and get answers. The blocker is almost never enthusiasm. It's data governance.
What "private" has to mean
Private AI is more than a checkbox. At minimum it means: customer data never leaves the customer's network boundary; the model has no path to exfiltrate what it reads; and every AI action against sensitive data is logged like any other privileged operation.
A practical starting point
Begin with retrieval over a bounded, well-governed corpus - your own operational knowledge - rather than open-ended generation. Keep a human in the loop for anything consequential, and treat the AI's access to data with the same just-in-time discipline you'd apply to a human administrator.
Done this way, AI becomes a force multiplier for security operations instead of a new class of data-exposure risk.