
Trends
The Case for Just-in-Time Everything
Standing privilege is a liability on the balance sheet of risk. Here's where just-in-time access is heading across identity, cloud, and data.
Zenxsys Team · August 28, 2026 · 6 min read
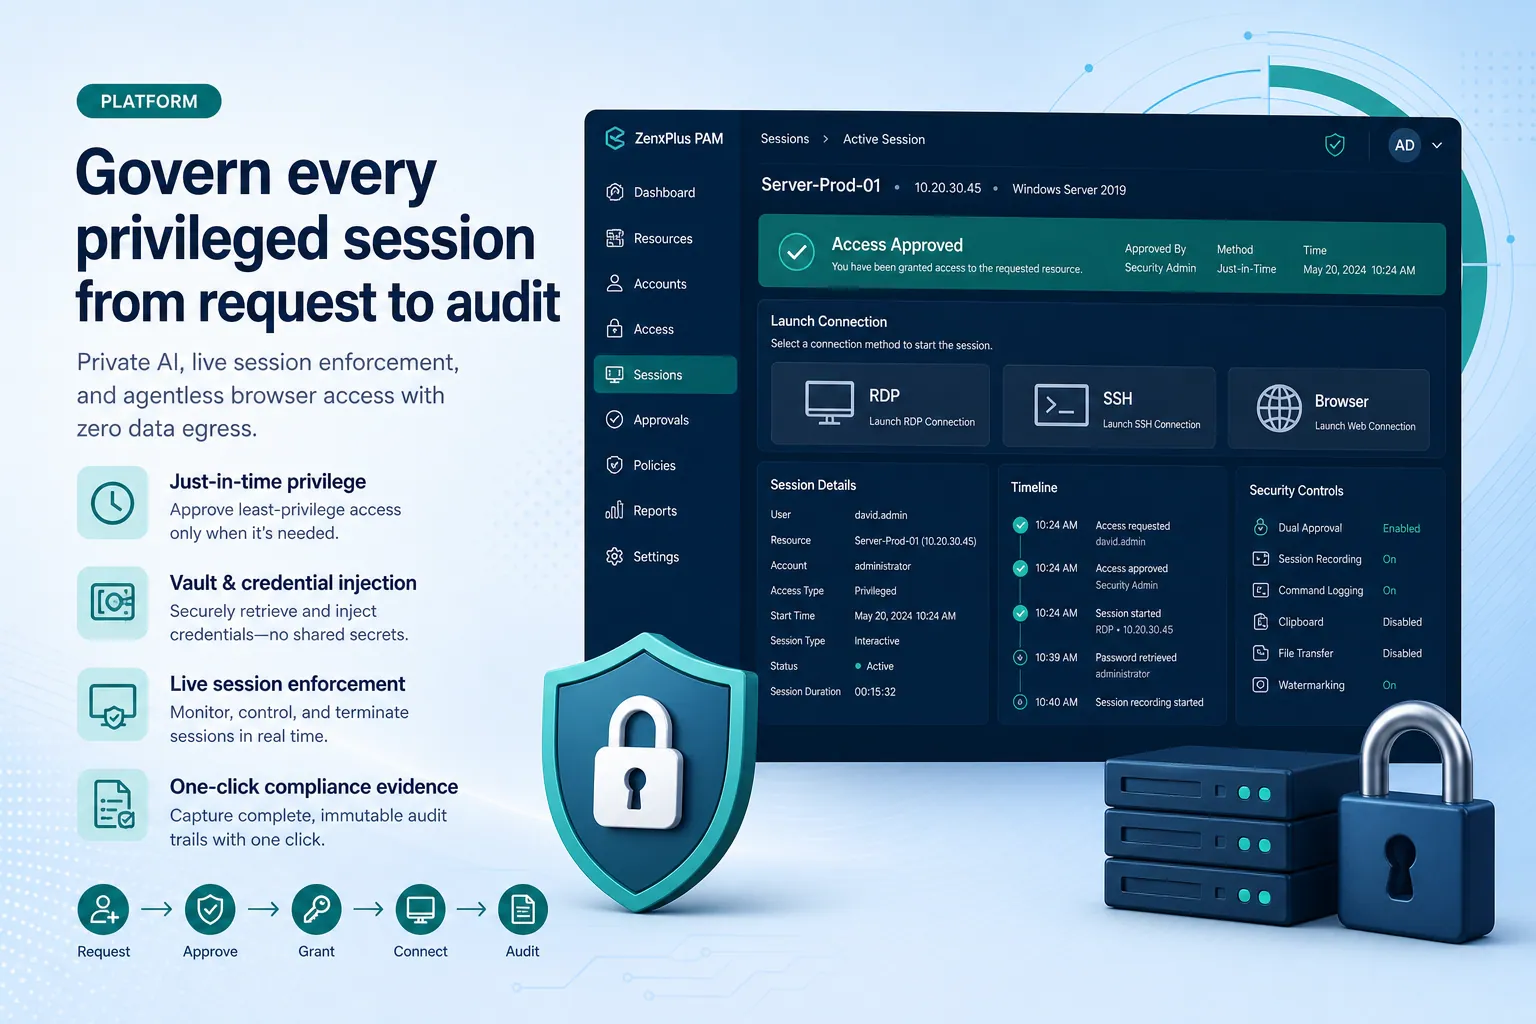
Every standing privilege is a bet that the account will never be compromised and the person will never make a mistake. That's a bet most organizations lose eventually.
From roles to requests
The industry is moving from role-based access - where privilege is a property of who you are - to request-based access, where privilege is a property of what you're doing right now. Access is requested, approved, used, and expired, leaving no residue.
Where it's spreading
Just-in-time started in privileged access management but is now showing up across the stack: JIT cloud entitlements, JIT database access, and JIT access to sensitive data sets. The common thread is the same - shrink the window in which any credential is useful to an attacker.
The end state isn't zero access. It's zero standing access: nothing is on by default, everything is granted deliberately, and everything expires on its own.