
Perspective
Why Vendor Access Is the New Perimeter
Third-party and contractor access is where most privileged risk now lives. Here's how to close the gap without slowing anyone down.
Zenxsys Team · September 10, 2026 · 5 min read
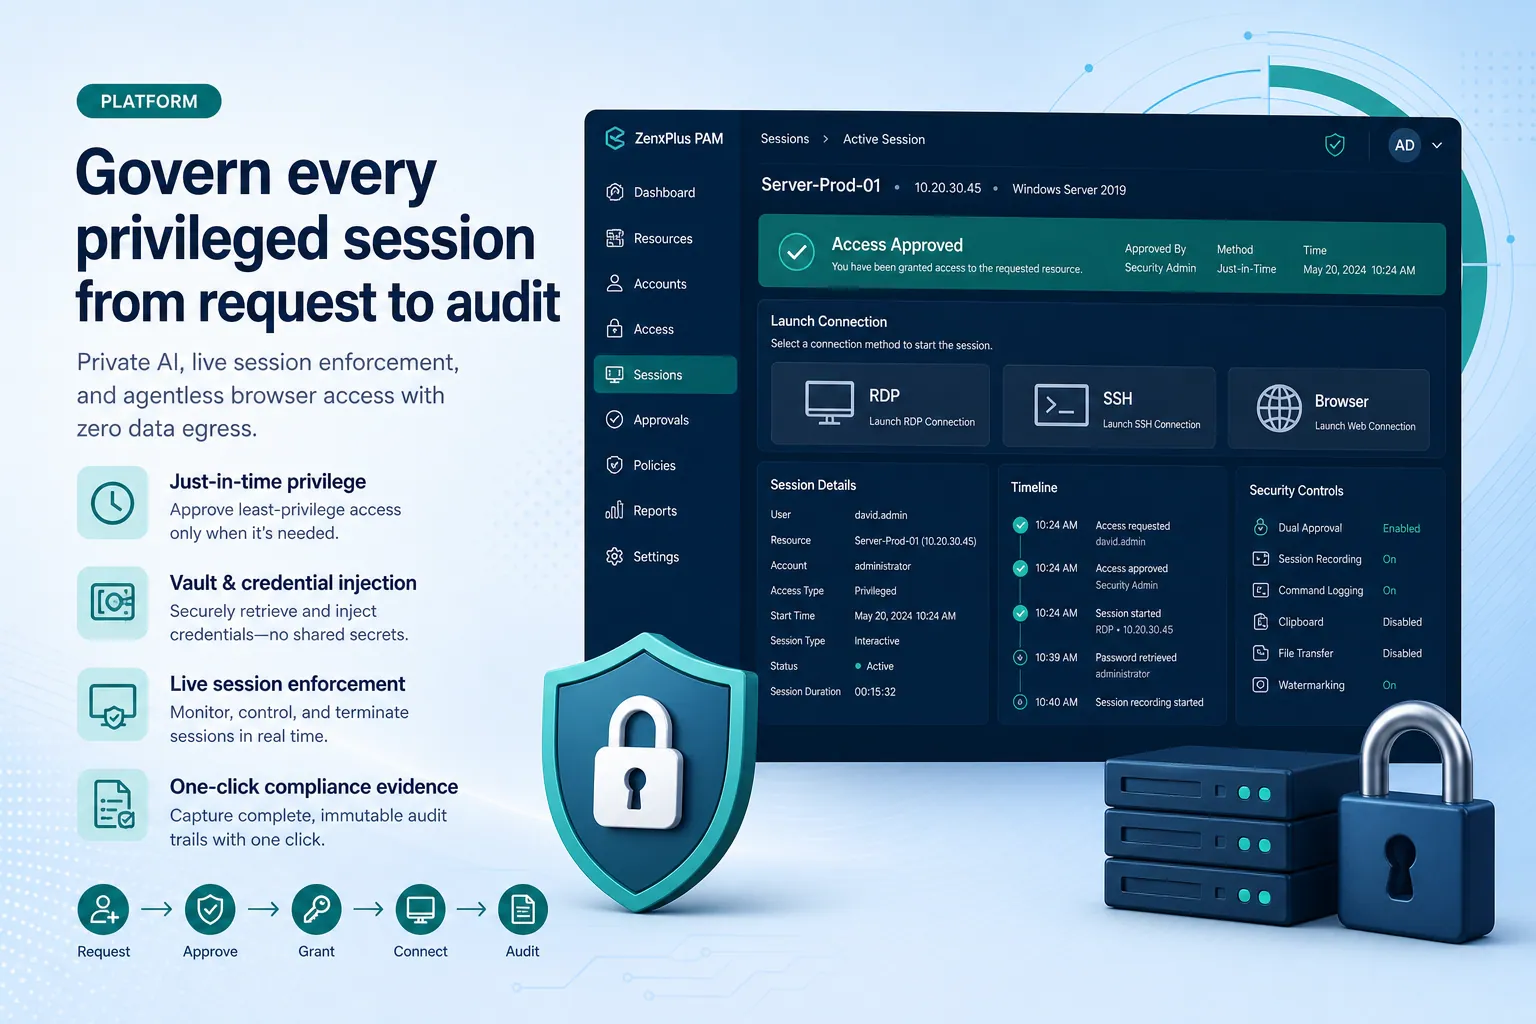
For years security teams built their defenses around employees: provision an account, assign a role, review it at offboarding. But the people touching your most sensitive systems today are increasingly not your employees. They are contractors, managed service providers, implementation partners, and vendor support engineers.
The access you can't see
Vendor access tends to be granted quickly, under deadline pressure, and rarely revisited. A support engineer gets a shared credential to "just fix the issue." A contractor keeps VPN access months after the project ends. Each of these is a standing door into your environment that no one is watching.
Three principles that close the gap
- Just-in-time, not standing. Grant vendor access for a specific task and a specific window, then revoke it automatically.
- Broker the session, don't hand over the keys. Vendors should work through a brokered session where credentials are vaulted and never exposed.
- Record everything. Every privileged vendor session should produce an audit-ready recording, so you can answer "who did what" in seconds, not weeks.
Treating vendor access as a first-class perimeter - governed, time-boxed, and fully audited - is one of the highest-leverage moves a security team can make this year.